

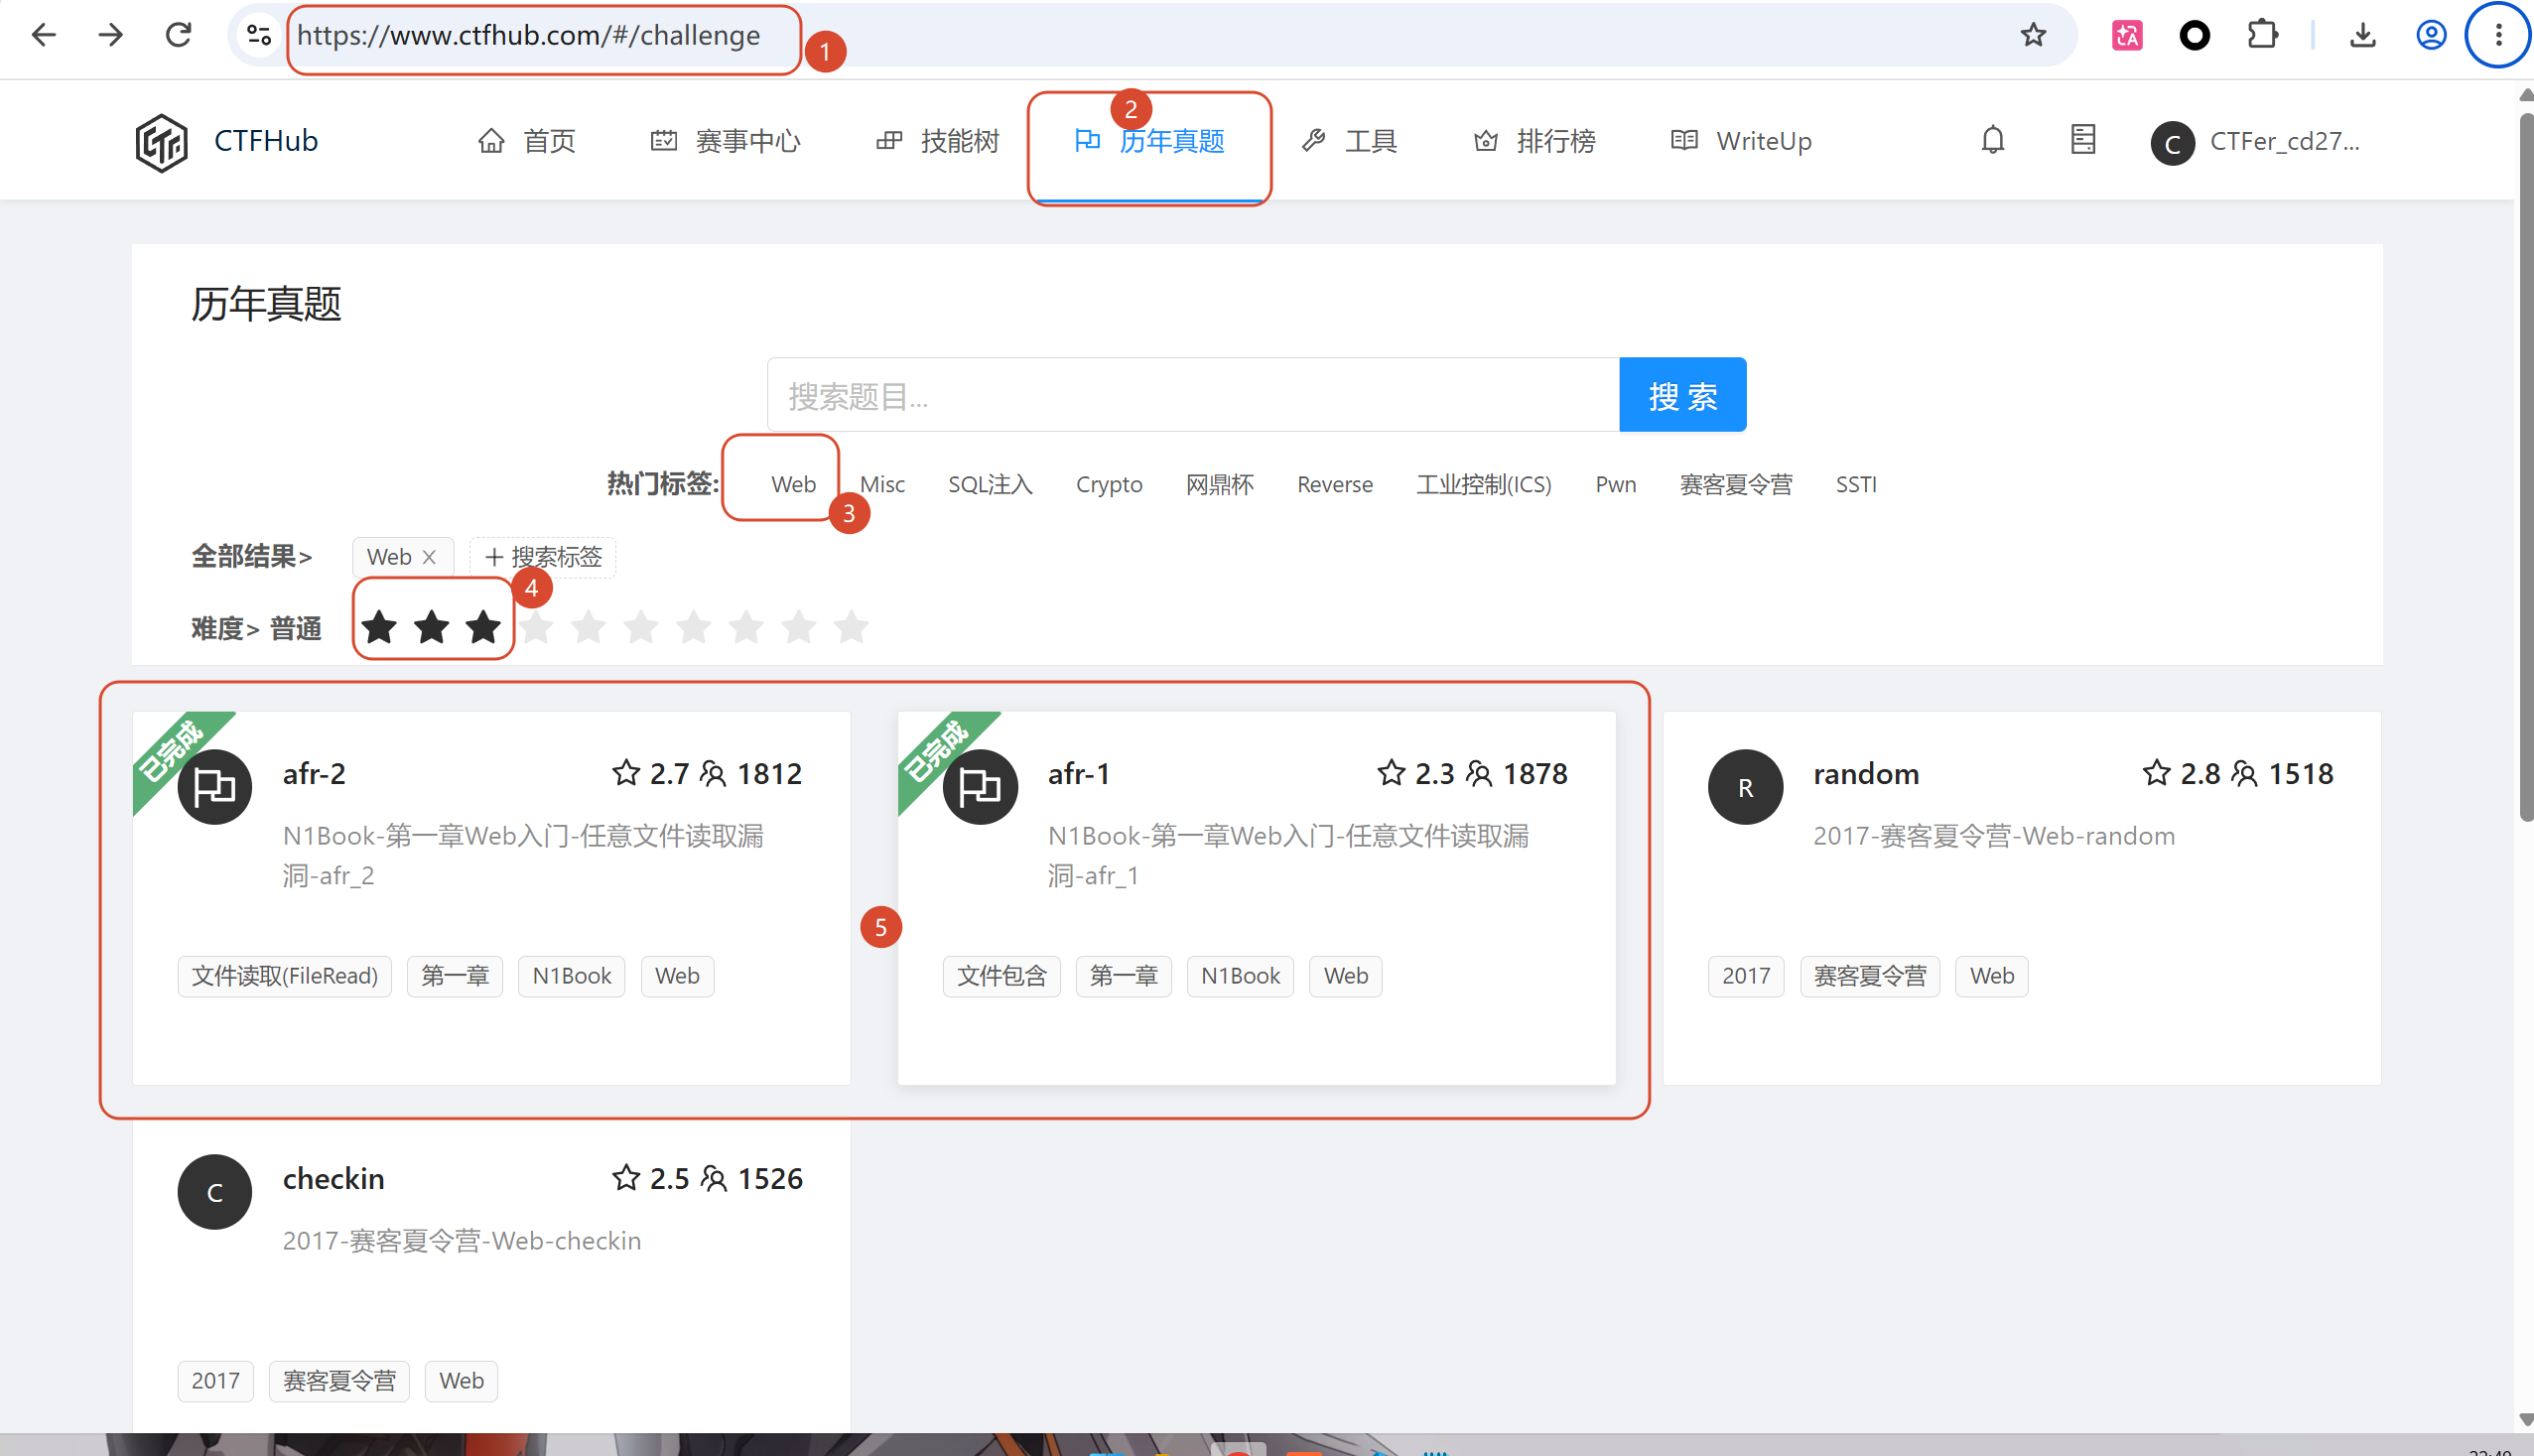
靶场链接
https://www.ctfhub.com/#/challenge
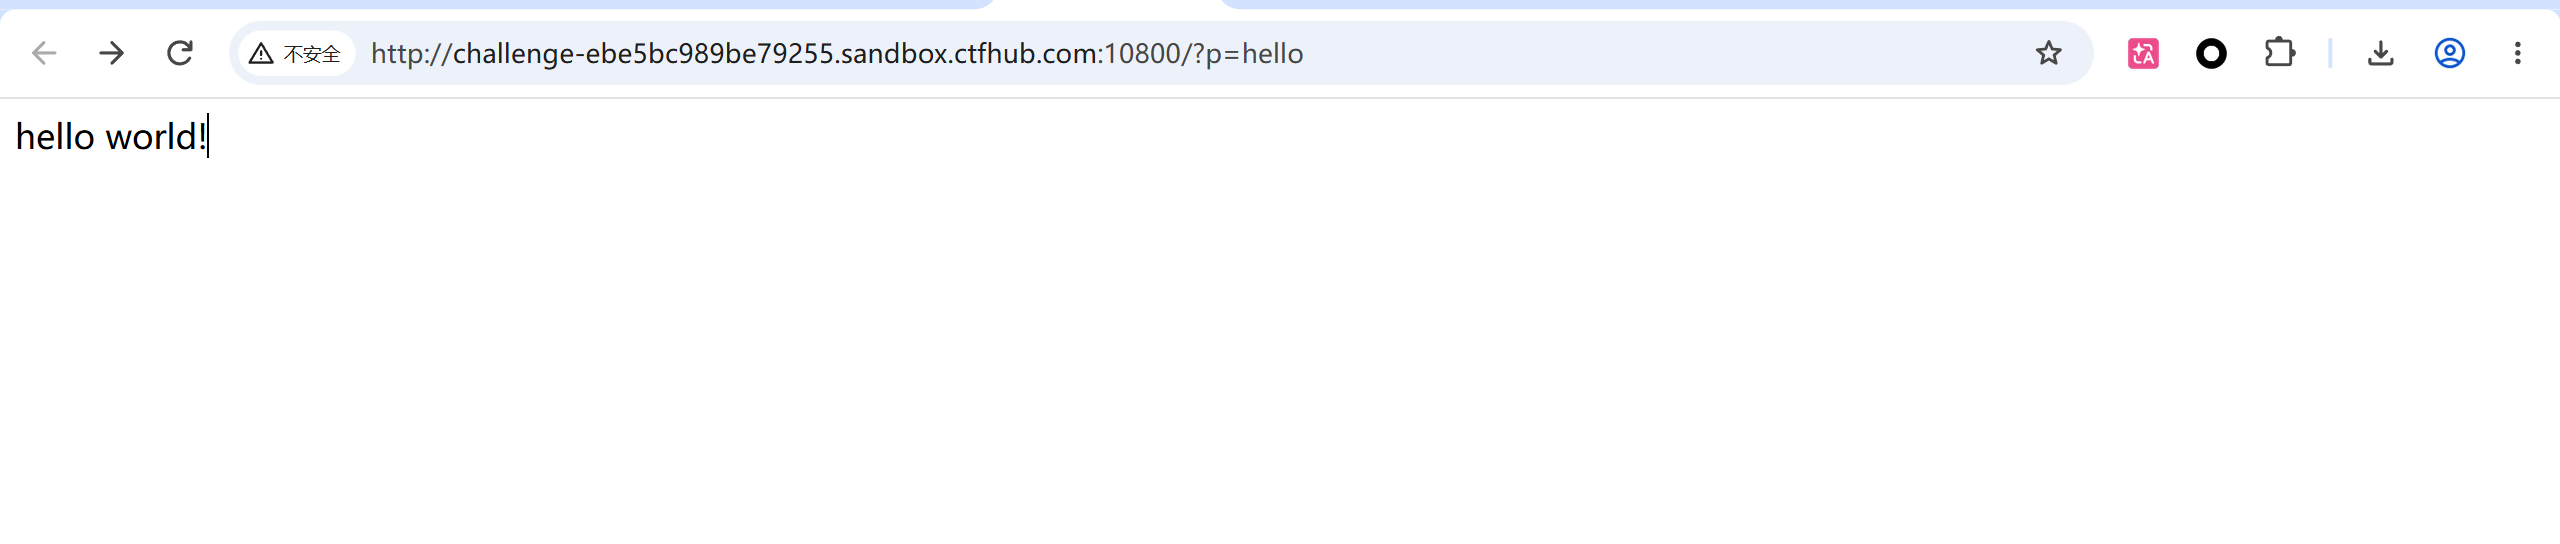
afr-1打开看到
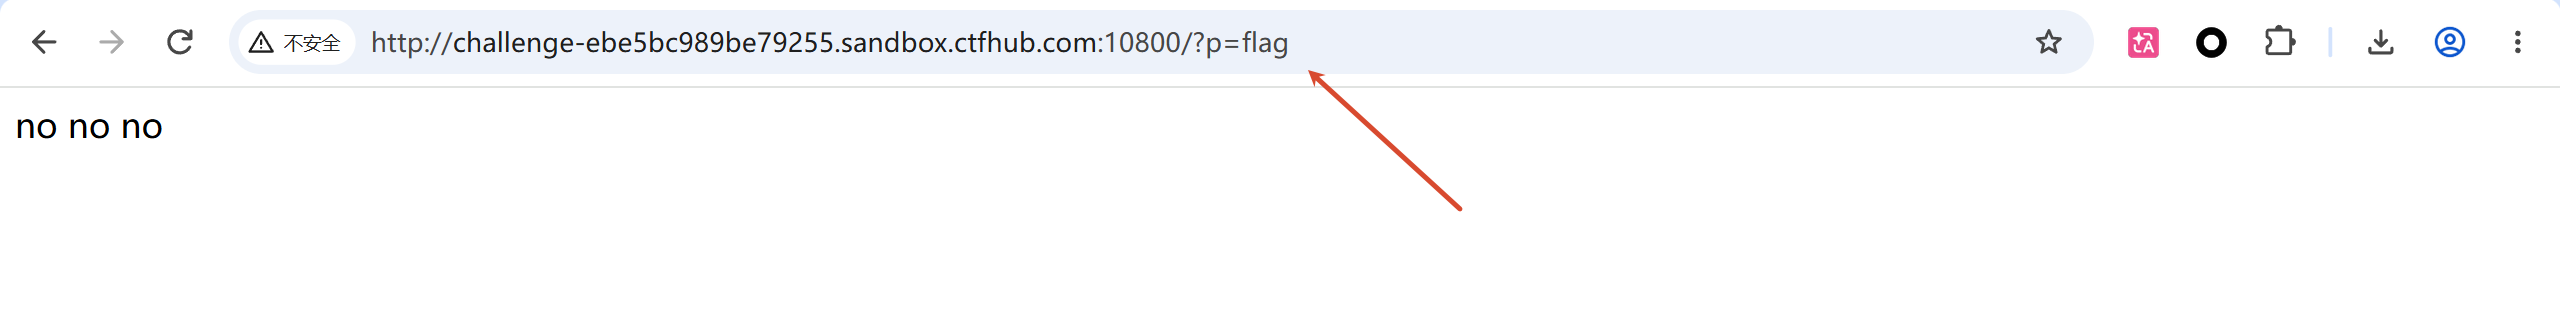
尝试直接访问flag,不让访问,但是可以确定flag就在这个位置
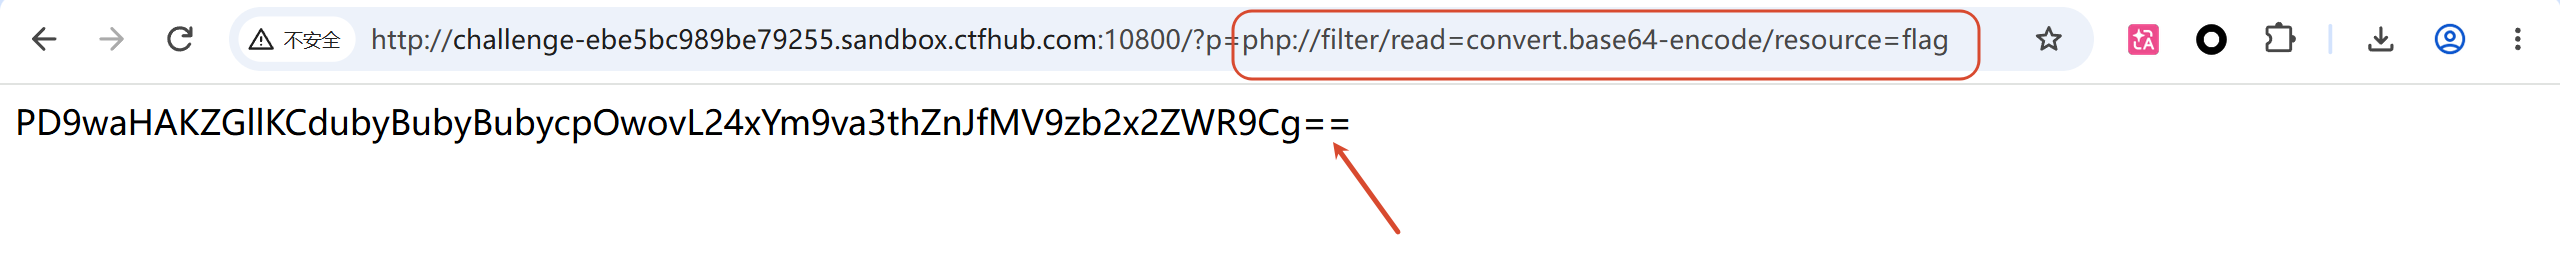
使用php任意文件读取方法尝试读取flagphp://filter/read=convert.base64-encode/resource=flag,得到了一个base64编码的字符串
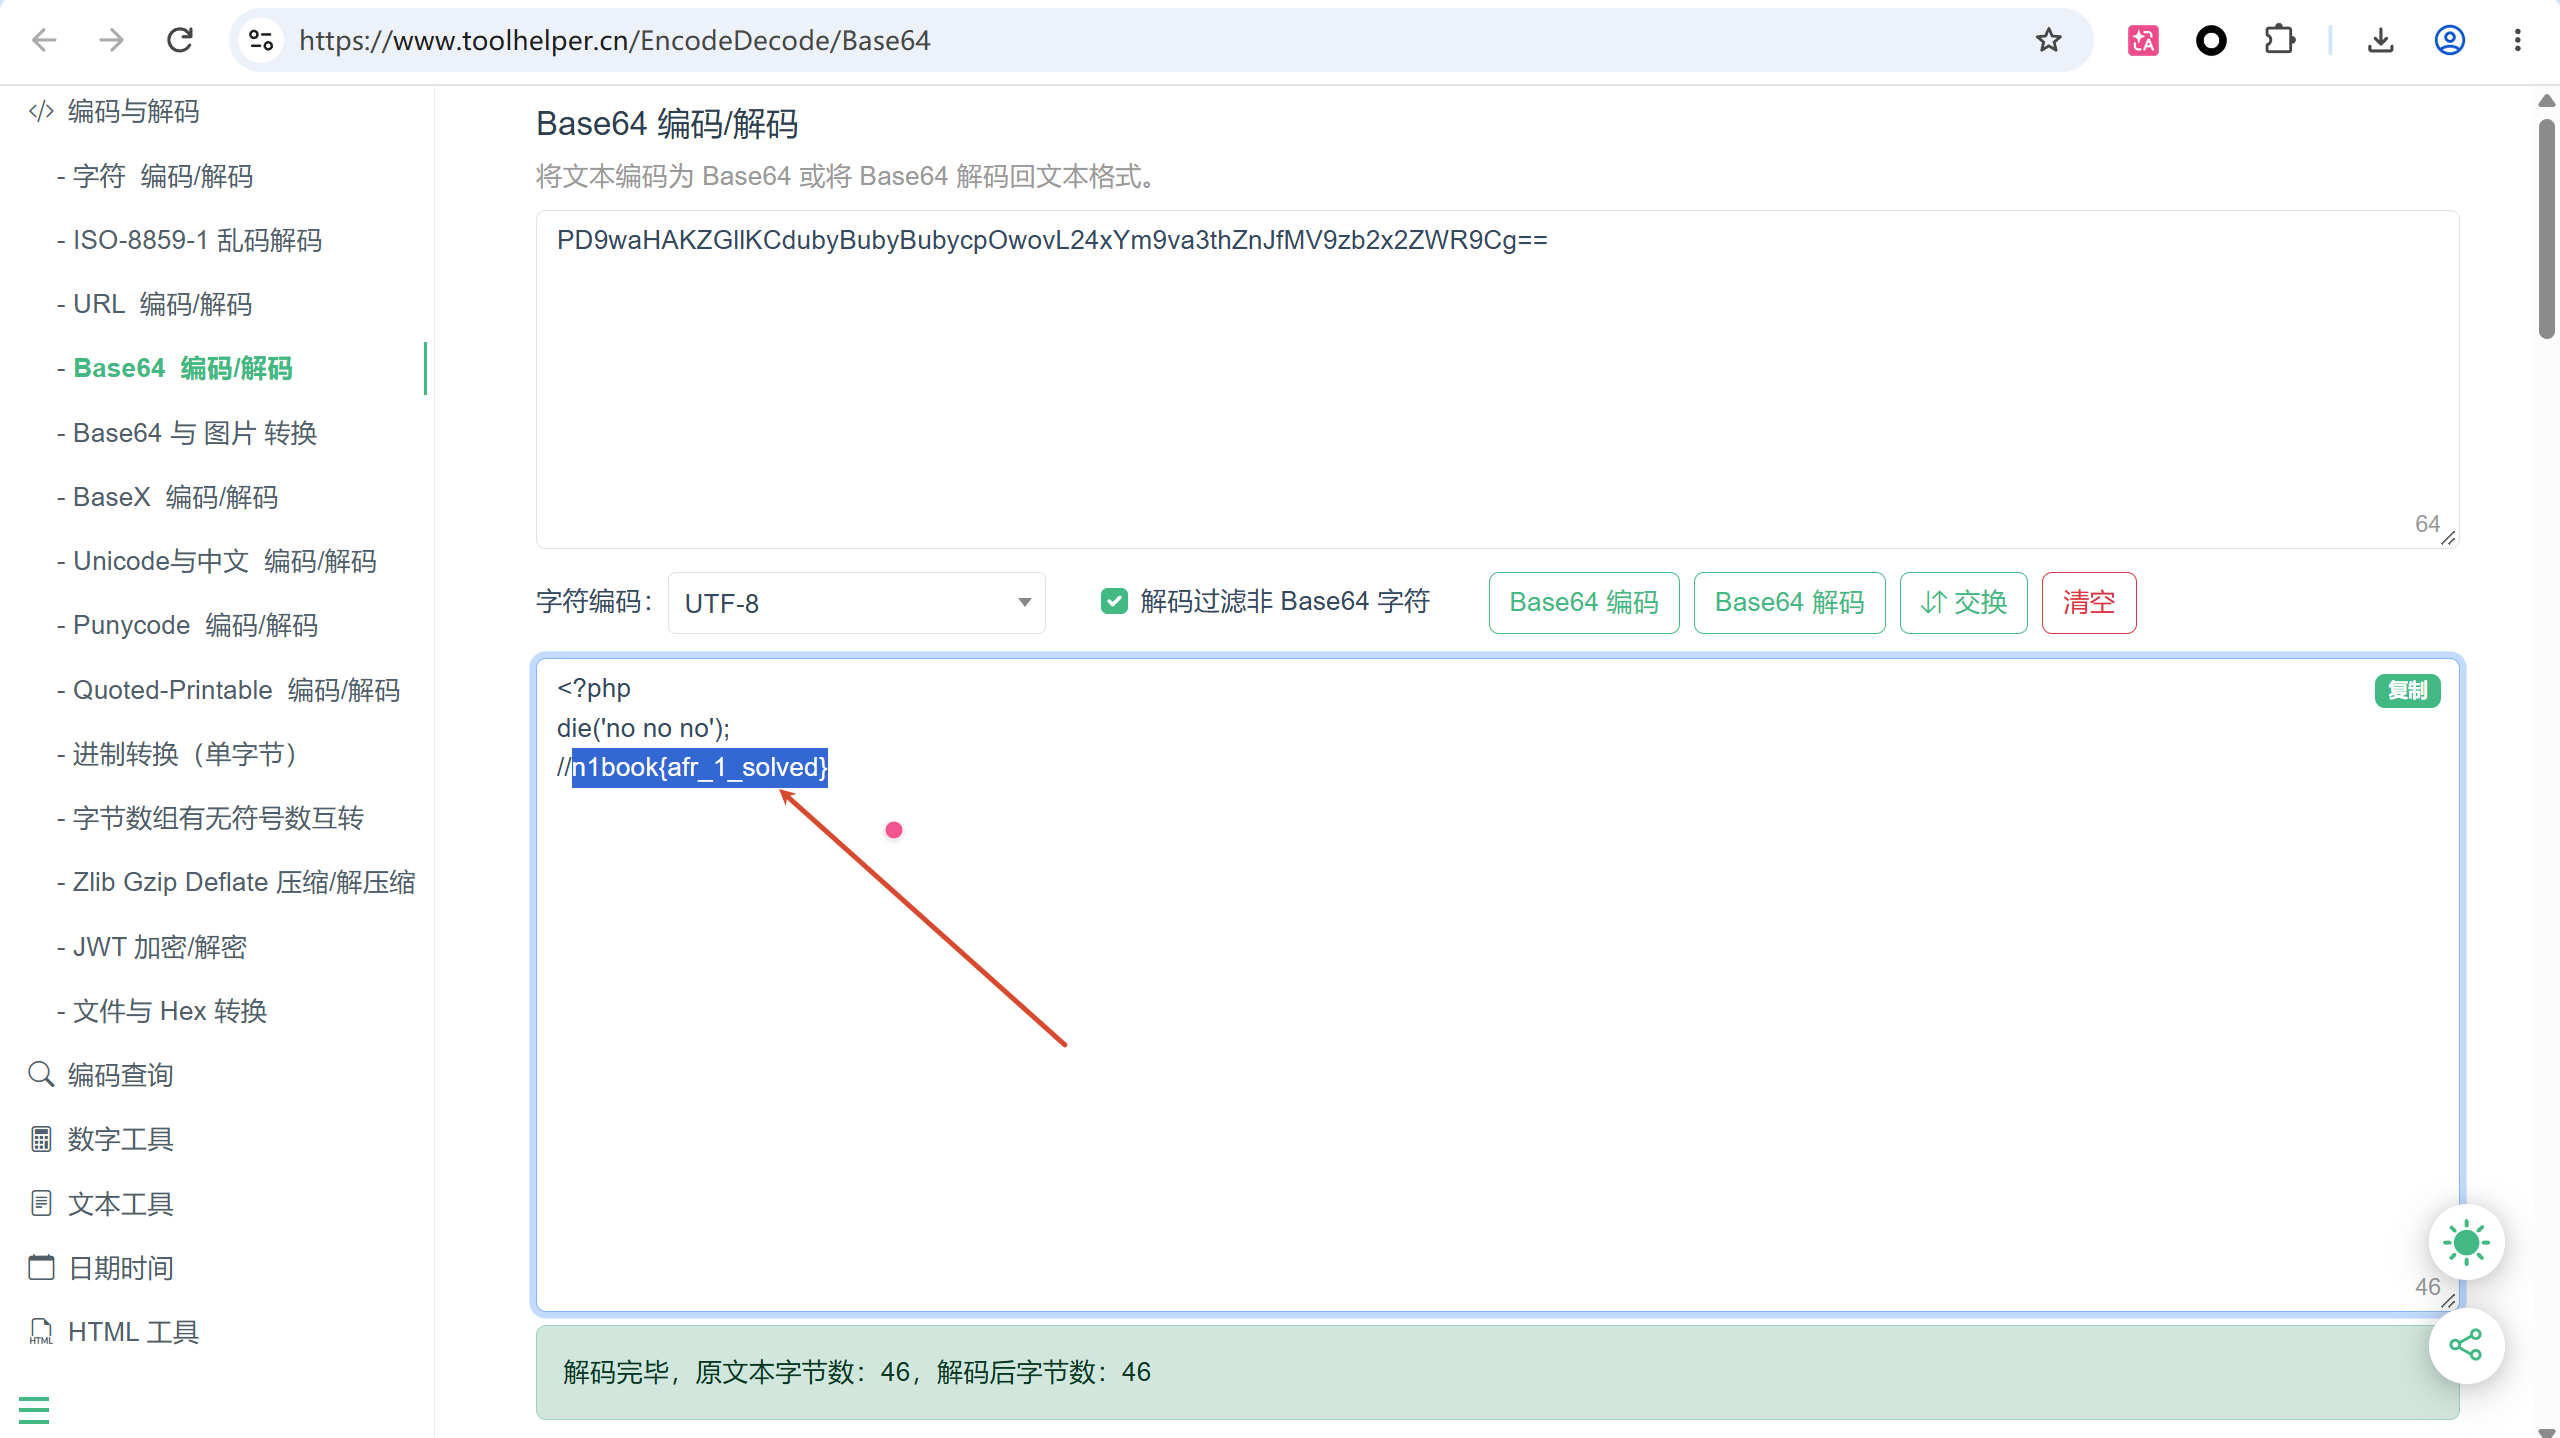
解码得到flag
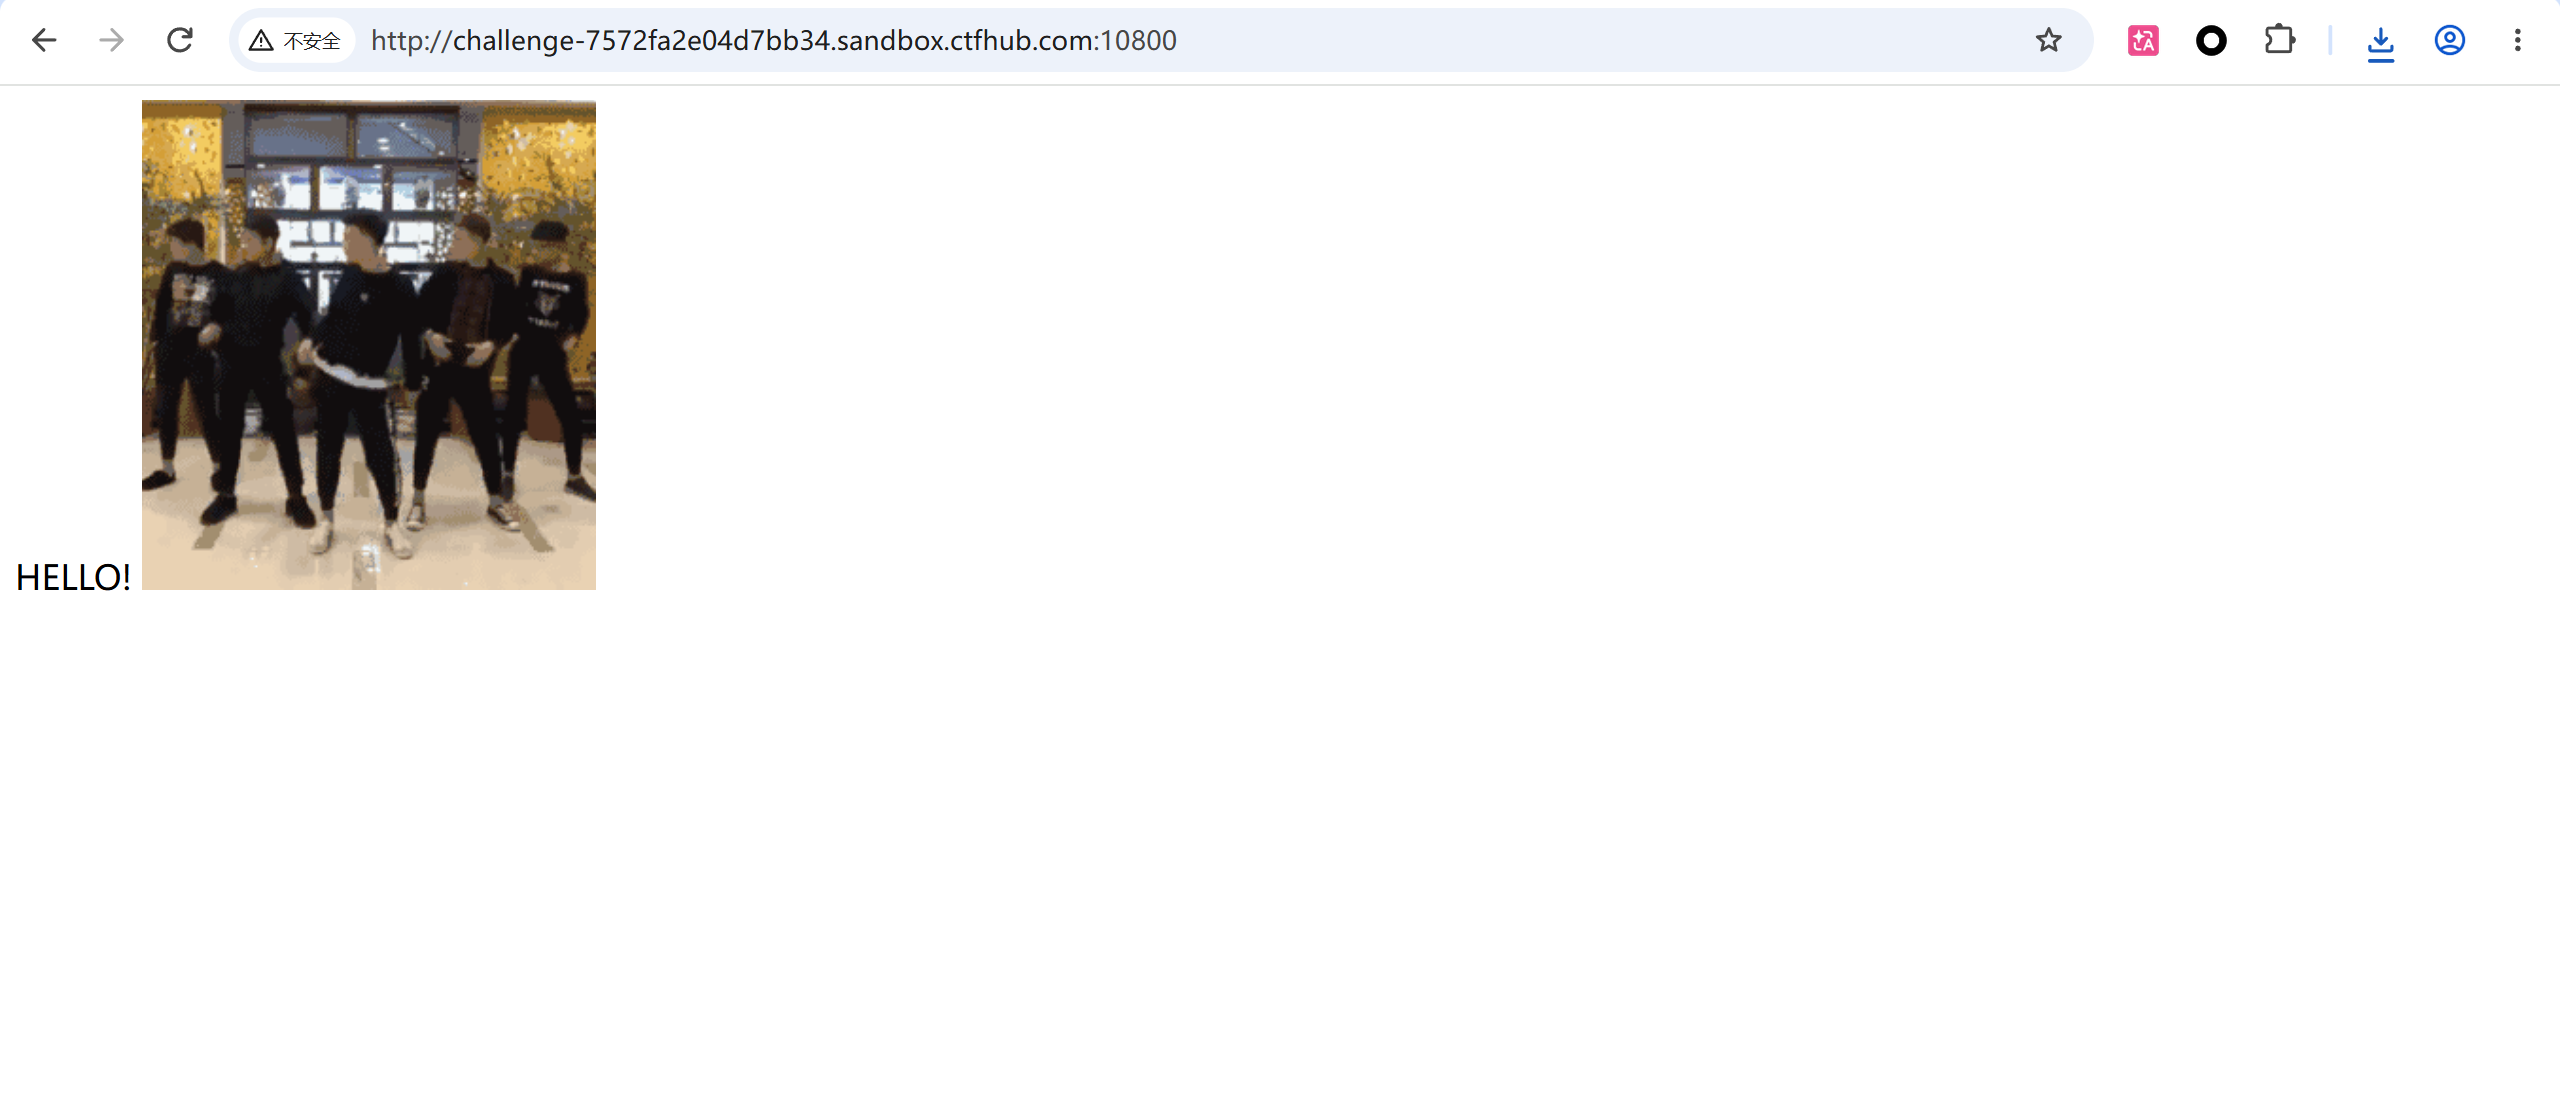
afr-2打开看到
右键图片在新标签页打开
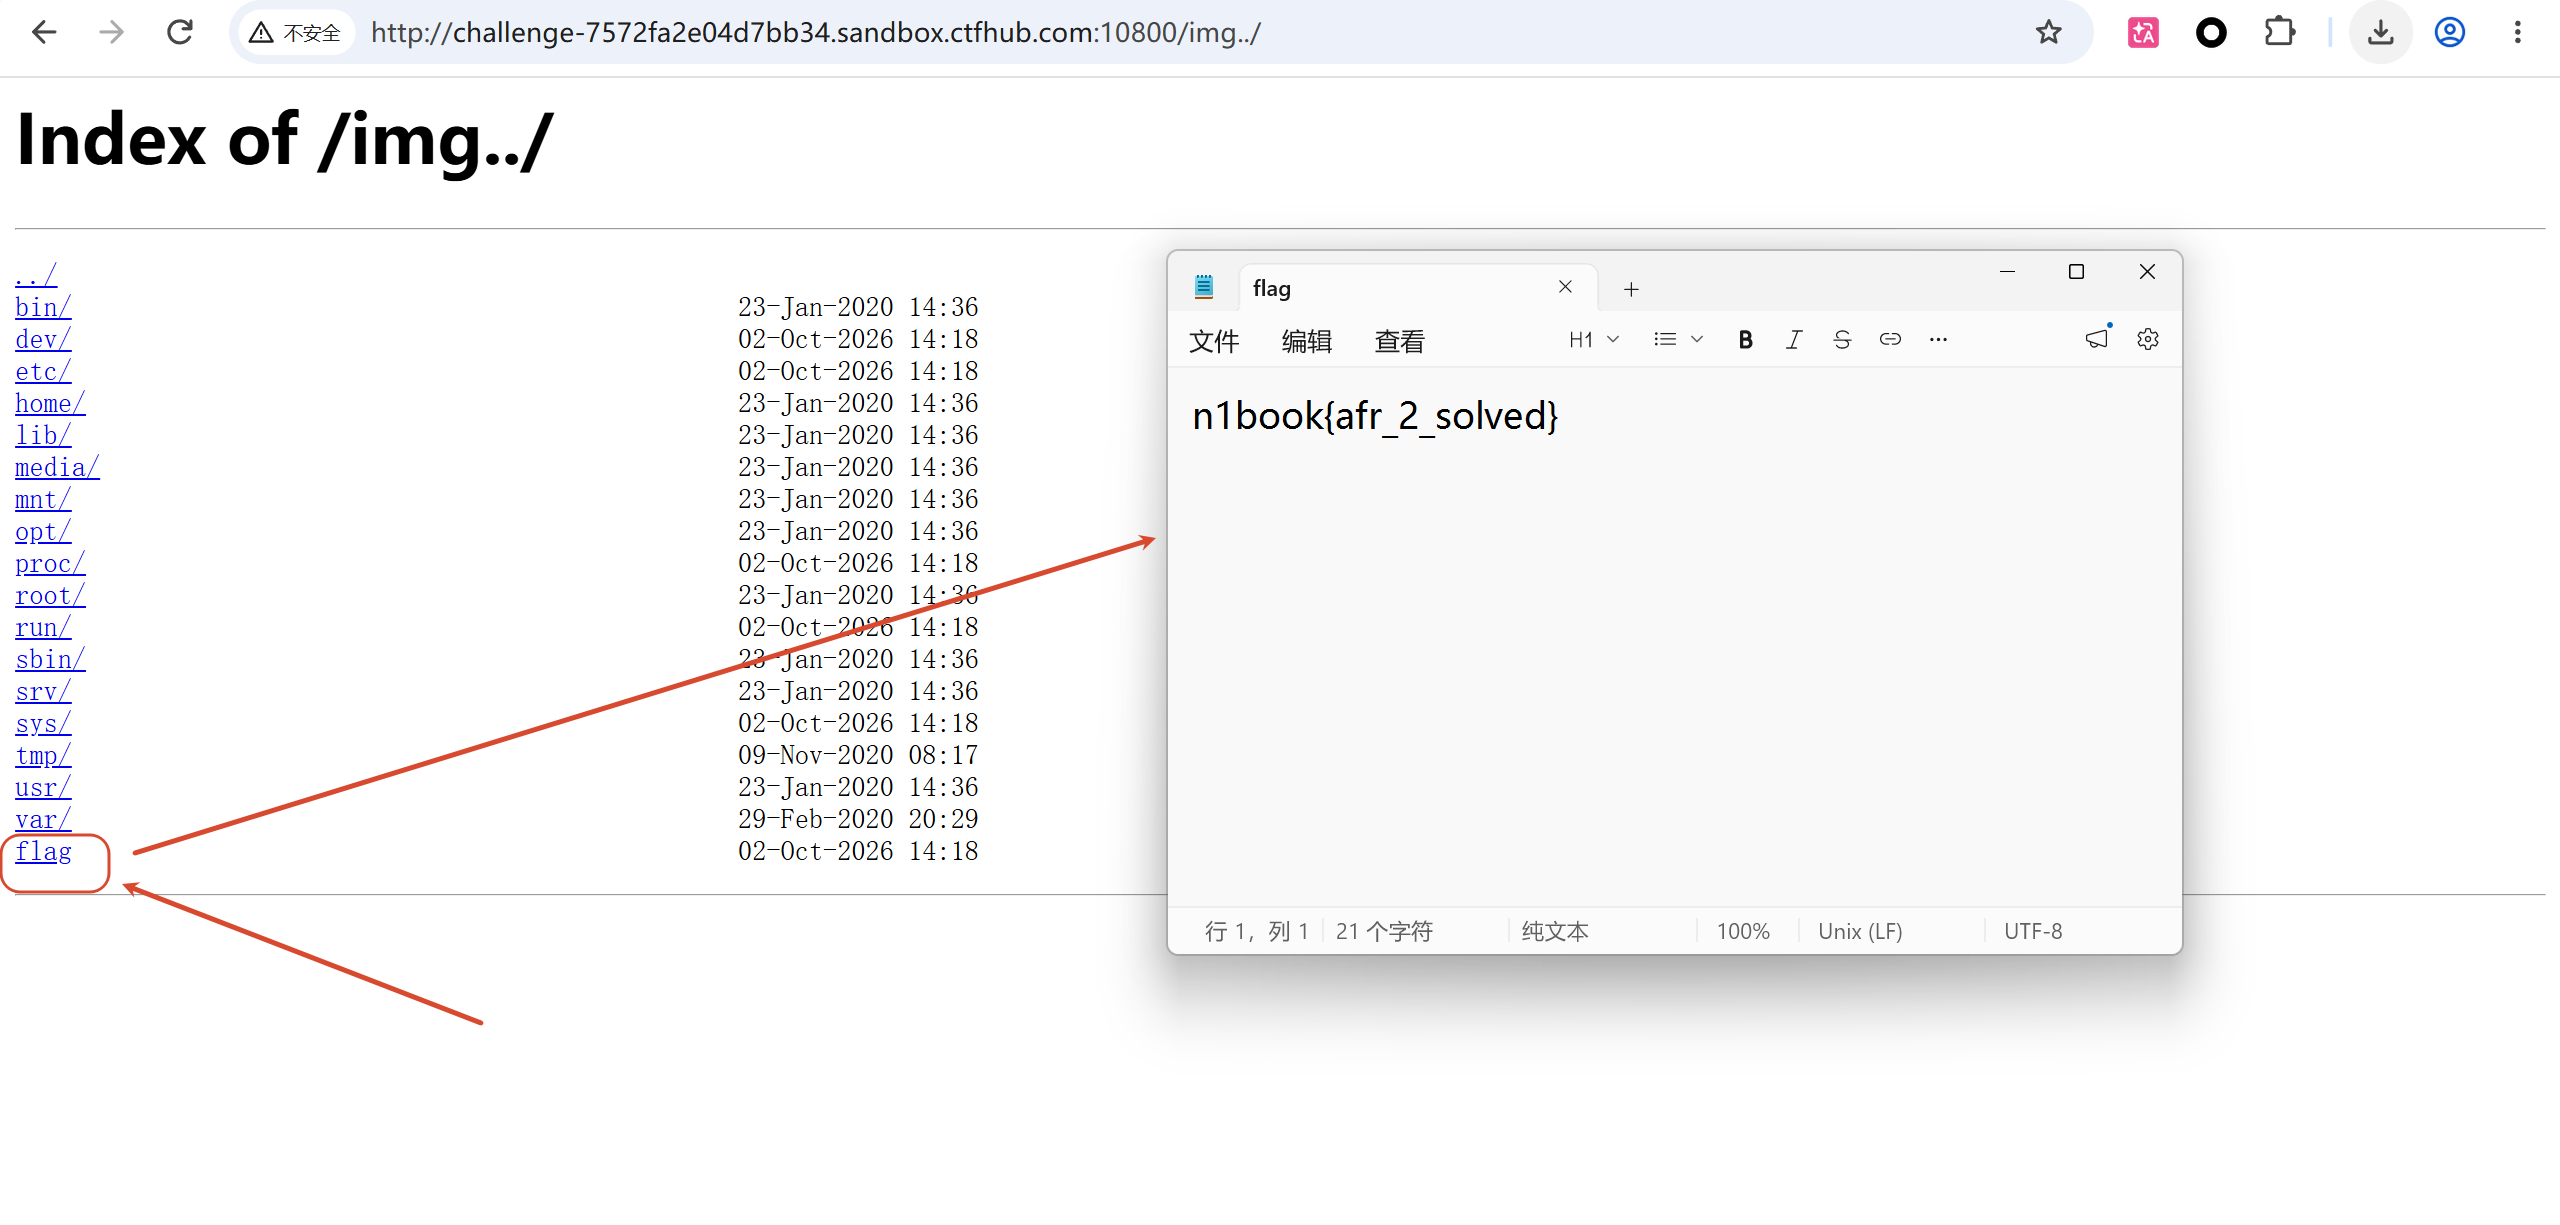
题目提示是考验任意文件下载,尝试访问其他文件夹http://challenge-7572fa2e04d7bb34.sandbox.ctfhub.com:10800/img../成功找到flag点击下载打开得到答案
评论 (0)